Who Should Attend this ISO 27001 Lead Auditor Course?
Our ISO 27001 Lead Auditor Course is designed for professionals responsible for auditing, evaluating, and overseeing Information Security Management Systems (ISMS). The following professionals can benefit from this course:
- Information Security Managers
- Compliance Officers
- Auditors
- Risk Managers
- Cybersecurity Engineers
- Compliance Officers
- Data Protection Officers
Prerequisites for the ISO 27001 Lead Auditor Course
There are no formal prerequisites to attend this ISO 27001 Lead Auditor Course. However, familiarity with information security and ISO 27001 standards can be beneficial for the delegates.
ISO 27001 Lead Auditor Course Overview
ISO 27001 Lead Auditor Training provides in-depth knowledge of auditing Information Security Management Systems in line with ISO/IEC 27001 standards. Delegates learn auditing principles, risk assessment approaches, ISMS requirements, and techniques for evaluating conformity and audit evidence.
Delegates develop the ability to plan, conduct, and manage ISMS audits confidently. They strengthen their skills in collecting evidence, evaluating findings, preparing audit reports, communicating conclusions, and supporting effective audit follow-up activities.
This 5-Day course offered by The Knowledge Academy equips delegates to apply structured auditing techniques in professional environments. They will be better prepared to conduct ISO 27001 audits, classify findings, report audit results, and contribute to the continual improvement of an organisation’s ISMS.
ISO 27001 Lead Auditor Course Objectives
- To understand the principles and requirements of ISO/IEC 27001 and ISMS auditing
- To plan and conduct ISMS audits using structured auditing approaches
- To evaluate audit evidence and assess conformity with ISO 27001 requirements
- To identify, classify, and communicate audit findings effectively
- To understand Information Security risk assessment and risk treatment approaches
- To develop skills in reporting audit results and supporting follow-up activities
Learning Outcome of this ISO 27001 Lead Auditor Course
Upon completing this ISO 27001 Lead Auditor Course, delegates will be able to plan, conduct, report, and follow up on ISO 27001 audits. They will also be able to evaluate audit evidence, classify findings, assess ISMS performance, and identify opportunities for corrective action and continual improvement.
Career Benefits of this ISO 27001 Lead Auditor Course
Our ISO 27001 Lead Auditor Course develops specialised knowledge of ISMS auditing principles, audit procedures, and ISO/IEC 27001 requirements. These capabilities support professional development in information security auditing and compliance. The following are some of the key career benefits:
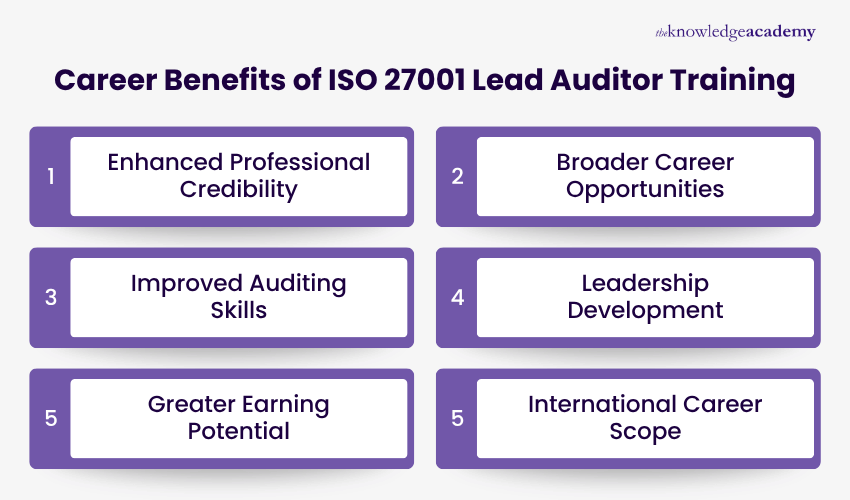
- Enhanced Professional Credibility: Build recognised expertise in ISO 27001 requirements, ISMS auditing, and information security practices.
- Broader Career Opportunities: Develop skills relevant to roles such as Lead Auditor, Information Security Consultant, Compliance Manager, and Risk Management Specialist.
- Improved Auditing Skills: Strengthen your ability to plan audits, collect evidence, identify nonconformities, prepare reports, and support follow-up actions.
- Leadership Development: Build confidence in leading audit activities, coordinating audit teams, and supporting organisations through certification and compliance requirements.
- Greater Earning Potential: Advanced ISO 27001 auditing skills can strengthen your professional profile and support progression into higher-responsibility information security and compliance roles.
- International Career Scope: ISO 27001 is globally recognised, helping professionals apply their auditing and information security knowledge across different industries and international environments.





 If you miss out, enquire to get
yourself
on the waiting list for the next day!



 If you wish to make any changes to your course, please


