


We may not have the course you’re looking for. If you enquire or give us a call on 01344203999 and speak to our training experts, we may still be able to help with your training requirements.
Cyber Security Awareness: Definition and Importance
ByThe Knowledge AcademyLast updated on: 01 October 2026
Cybersecurity awareness is a continuous process of educating employees about the dangers in cyberspace and teaching them how to act responsibly. It helps reduce the risk of cybersecurity incidents by improving employees’ ability to recognise and respond to threats. Learn how cyber security awareness can help protect your organisation.
What You Should Know
1. Every employee has a role in maintaining an organisation’s cyber security.2. Awareness works best alongside strong technical security controls.3. Phishing and social engineering remain key areas for employee awareness.4. Ongoing learning helps reinforce secure habits across the workplace.5. A strong security culture encourages safe behaviour and prompt incident reporting.
Imagine opening an email that appears to be from your bank, urging you to verify your account details immediately. Feeling a sense of urgency, you click the link, only to realise it was a phishing attempt! In today's digital world, cyber threats are constantly evolving, and cyber security awareness is no longer optional.
This blog explores cyber security awareness and its role in protecting against digital threats. We'll explore what it means to be cyber security aware and how this awareness can protect you, your devices, and your data from online threats.
Cyber security awareness equips you with the knowledge and skills to recognise common cyber threats and respond to them appropriately, helping protect your devices, data and online activities. So, buckle up and get ready to learn how to navigate the web with confidence!
What is Cyber Security Awareness?
Cyber security awareness involves both understanding and acting to protect a company's information assets. When employees are aware of cyber security, they comprehend cyber threats, their potential impact, and the necessary actions to mitigate risk and prevent cybercrime.
Promoting a cyber security culture in the workplace does not completely eliminate the risk of data theft or cybercrime. Malware has evolved, becoming increasingly sophisticated with each new strain, and this trend is expected to continue.
With cyber threats growing in complexity, companies must continuously adapt their security measures. Regular employee training, robust security protocols, and constant vigilance are essential to identify and mitigate vulnerabilities, reducing the risk of cyber-attacks. Human error remains a significant risk, potentially leading to severe penalties and substantial business damage.
Why is Cyber Security Awareness Important?
Despite strong security systems and policies, organisations can still experience breaches involving human actions, such as social engineering, credential misuse, and mistakes. At the same time, vulnerabilities in software and systems remain a major route for attackers, showing why cyber security awareness should complement strong technical security controls.
Cyber awareness educates employees about the malicious tactics used by cybercriminals, how they can become easy targets, how to identify potential threats, and how to avoid falling victim to these attacks. It equips employees with the knowledge and resources needed to detect and flag potential hazards before they cause any damage.
Trainer’s Insight
Cyber security awareness should not be treated as a substitute for technical security. The strongest approach combines informed employees with controls such as MFA, access management, secure configurations and timely software updates.
Common Types of Cyber-Attacks
Cyber-attacks can target systems, networks and users in different ways. Some common types of cyber-attacks include:
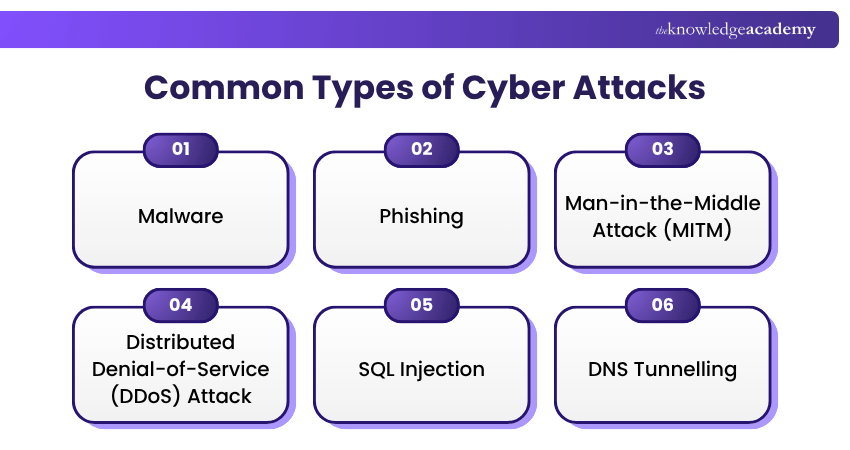
1) Malware
Malware is a type of programme that can perform several destructive functions. Some malware strains are meant to get persistent network access, while some are designed to spy on the user in order to steal passwords or other important data. Ransomware is a common type of malware that can encrypt a victim's files or systems and demand payment for restoring access.
How to prevent a Malware attack?
Preventing a malware attack is a difficult endeavour that requires a multi-pronged strategy. At least, you must:
a) Ensure that you have the latest anti-malware protection software installed
b) Ensure that employees are trained to identify fraudulent emails and websites
c) Use a strong password policy with Multi-factor Authentication (MFA)
d) Keep all software up-to-date
e) Control access to systems and closely adhere to the least-privilege concept
2) Phishing
A phishing attack occurs when an attacker tries to mislead an unsuspecting target into revealing sensitive information such as passwords, credit card information, intellectual property, etc. Phishing attacks are frequently sent in the form of an email pretending to be from a legitimate institution, such as your bank, the tax department, or another reliable source.
Phishing remains a common social engineering technique in which attackers impersonate trusted individuals or organisations to trick people into revealing information, opening malicious attachments or visiting fraudulent websites.
How to prevent a Phishing attack?
The techniques used to avoid phishing attacks are quite similar to preventing malware attacks. However, phishing attempts are mostly the result of a lack of attention. Security awareness training is an important part of phishing defence, but it should be combined with technical controls and simple reporting processes. Employees should know how to recognise suspicious messages, links and websites and how to report suspected phishing attempts quickly.
Think Before You Click
Before opening a link or attachment, check:✓ Do you recognise the sender?✓ Does the message create unusual urgency?✓ Does the link match the expected destination?✓ Is the request for sensitive information unusual?✓ Can you verify the request through another trusted channel?When in doubt, report the message rather than interact with it.
3) Man-in-the-Middle Attack (MITM)
A Man-in-the-Middle (MITM) attack happens when an attacker intercepts communication between parties to monitor communications, steal sensitive information or alter transmitted data. Encryption and secure communication protocols can significantly reduce the risk of successful interception.
How to prevent a Man-in-the-Middle attack?
If the communication protocols you employ do not support end-to-end encryption, consider connecting to your network over a Virtual Private Network (VPN), especially if you are accessing from a public Wi-Fi hotspot. Be cautious of fraudulent websites, suspicious pop-ups and certificate warnings. Check that websites use HTTPS, while remembering that HTTPS alone does not guarantee that a website is trustworthy.
4) Distributed Denial-of-Service (DDoS) Attack
A DDoS attack happens when an attacker floods a target server with traffic to disrupt and, perhaps, bring down the target. However, unlike a Denial-of-Service (DoS) attack originating from a limited source, a DDoS attack typically uses numerous compromised devices to generate traffic against the target.
How to prevent a DDoS Attack?
DDoS attacks can be difficult to prevent entirely, but organisations can reduce their impact through traffic monitoring, rate limiting, resilient infrastructure and dedicated DDoS mitigation services. A documented incident response plan can also help teams respond quickly when an attack occurs.
5) SQL Injection
SQL injection is a type of SQL database attack. SQL databases query data using SQL statements, commonly executed via an HTML form on a webpage. If the database permissions are not correctly specified, the attacker can use the HTML form to perform queries that create, read, edit, or remove data from the database.
How to prevent a SQL Injection attack?
SQL injection can be mitigated by using parameterised queries or prepared statements so that user-supplied data is treated as data rather than executable SQL. Input validation, appropriate database permissions and secure coding practices provide additional layers of protection.
6) DNS Tunnelling
DNS tunnelling is a technique that can abuse DNS queries and responses to establish covert communication channels, transfer data or support command-and-control activity.
How to prevent a DNS Tunnelling attack?
DNS tunnelling can be difficult to detect using basic security controls alone. Organisations can monitor DNS traffic for unusual patterns, restrict unnecessary DNS communications and use DNS security or network monitoring tools to identify suspicious activity.
Learn the fundamentals of cyber security. Sign up for our Certified Cyber Security Professional (CCS-PRO) Course now!
Essential Elements of Cyber Security Awareness
Over the years, cyber security awareness training has evolved from being primarily for security professionals to encompassing IT administrators and all employees. The scope of these programmes may vary based on employee numbers, awareness levels, budget, and other factors. Regardless of scope, certain essential courses should be included in every cyber security awareness training:
1) Email Security
Email is an essential communication tool for businesses but also a major entry point for cybercrime, including phishing, ransomware, malware, and Business Email Compromise (BEC). Email security training is essential to protect employees and the business from malicious email attacks. This training helps employees recognise unsafe links and attachments.
2) Phishing and Social Engineering
The human element is a primary target for cyber attackers. Social engineering attackers exploit human behaviour and emotions to manipulate their targets into taking actions like disclosing sensitive information, granting system access, sharing credentials, or transferring funds. Training employees to detect the warning signs of phishing and social engineering attacks significantly reduces the risk of falling victim to these scams.
3) Ransomware and Malware
Malware, such as ransomware, often infiltrates organisations via phishing emails. Ransomware awareness training educates employees on how these attacks are executed, the tactics used by threat actors, and the preventive measures they can take to combat rising ransomware threats.
4) Physical Security
Maintaining physical security is crucial, even in the digital age. Employees should be aware of the risks of leaving sensitive documents, unattended computers, and passwords around the office or home workspace. Implementing a 'clean-desk' policy can significantly reduce the threat of unattended documents being stolen or copied, thus enhancing overall security.
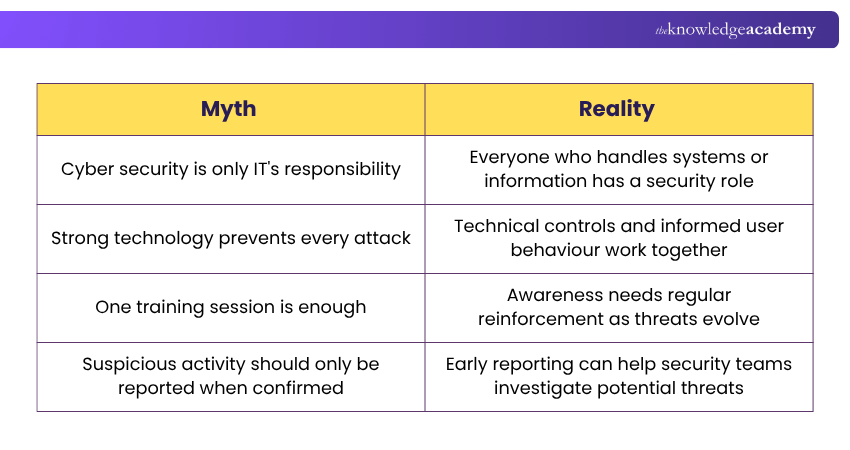
Myth vs Reality
Cyber Security Awareness Challenges
Here are some of the most common challenges to spreading cyber security awareness:
a) Mitigating Cybercrime Risks: While cyber awareness cannot eliminate cybercrime, it is crucial for reducing potential risks. Many organisations provide security awareness training, but successful breaches show that awareness programmes need to be reinforced by effective processes and technical controls.
b) Rapidly Evolving Threats: Cybercriminals continuously develop new attack methods, making it challenging to keep training programs current. Cyber security training materials can quickly become outdated, as knowledge and skills effective today may not suffice against tomorrow’s threats.
c) Manual Development Process: Creating cyber security awareness programs is often a manual process, unless a fully managed program is used. This involves selecting security content, creating resources, and testing training materials and tools, which can be time-consuming and burdensome.
d) Employee Engagement: Engaging employees in cyber security training is always a challenge. Repetitive curriculum, information overload, lengthy courses, and complex content can discourage participation, making it difficult to maintain interest and involvement.
Best Practices for Improving Cyber Security Awareness
Here are some easy steps you can take to improve security and reduce the risk of cybercrime at your organisation:
1) Educate Staff
Employees remain an important part of an organisation's security posture because attackers frequently use phishing, social engineering and stolen credentials. Regular awareness training can help staff recognise suspicious activity, follow security procedures and report potential incidents promptly.
2) Teach Employees to Handle Sensitive Data Safely
Employees should understand how to identify, store, share and dispose of sensitive information securely. Training should also reinforce the use of approved systems, appropriate access controls and clear procedures for reporting accidental data exposure.
3) Reinforce Awareness Regularly
Provide regular refresher training, practical examples and clear security reminders to help employees recognise emerging threats and apply safe behaviours consistently.
Quick Cyber Security Awareness Checklist
✓ Use strong authentication and follow access policies✓ Treat unexpected links and attachments cautiously✓ Handle sensitive information through approved systems✓ Keep devices and software updated✓ Report suspicious activity promptly✓ Participate in refresher training and security exercises✓ Follow organisational security procedures consistently
Enhance ability to identify, assess, and manage evolving cyber risks effectively with our Cyber Security Training – Join now!

The Knowledge Academy develops accessible learning content across Project Management, IT, Cybersecurity, Data Science, Business Analysis, HR, Accounting and Finance, Leadership and Health and Safety. Its resources combine subject research with clear explanations to help professionals build practical knowledge across a wide range of disciplines.
View Detail

 If you wish to make any changes to your course, please


