



We may not have the course you’re looking for. If you enquire or give us a call on 01344203999 and speak to our training experts, we may still be able to help with your training requirements.
Home
 Resources
IT Security & Data Protection
Cyber Security Analytics: Techniques, Benefits and How It Works
Resources
IT Security & Data Protection
Cyber Security Analytics: Techniques, Benefits and How It Works
Cyber Security Analytics: Techniques, Benefits and How It Works
ByNilotpal SarmahLast updated on: 06 October 2026
This blog on cyber security analytics explores how data are collected and analysed to detect cyber threats, support response, and enhance data protection.
At a Glance
1. Cyber security analytics collects and analyses security data to detect suspicious activity and potential threats earlier.2. Its main purposes are detecting threats, assessing their severity and supporting the response.3. Anomaly detection, behavioural analytics, network traffic analysis, threat intelligence correlation and risk scoring are the core techniques it relies on.4. A typical process moves from collecting security data to correlating it, then prioritising threats for investigation and response.5. Key benefits include better threat visibility, faster investigation, quicker response and more efficient security operations.
Trade secrets, R&D data and other sensitive information hold significant value and, if exposed, can seriously affect an organisation, which makes them an attractive target for attackers. Attackers keep refining their techniques, which makes cyber security a growing investment priority for many organisations.
According to PwC's 2026 Global Digital Trust Insights survey, as reported by Statista, 36 per cent of surveyed business leaders worldwide named AI among their top three cyber investment priorities for 2026, while 34 per cent named cloud security.
With threats evolving this quickly, organisations need effective ways to monitor, detect and respond to suspicious activity. Cyber security analytics supports this by analysing security data for the patterns and anomalies that individual alerts can miss, helping teams detect threats earlier and improve security operations.
What is Cyber Security Analytics?
Cyber security analytics involves collecting and analysing security data to identify patterns, anomalies, and potential threats. It supports proactive threat detection, investigation, risk assessment, and incident response.
Rather than treating each alert in isolation, it correlates security events over time and applies techniques such as machine learning and behavioural analytics. This builds a fuller picture of what is happening across systems, so teams can separate genuine threats from routine activity.
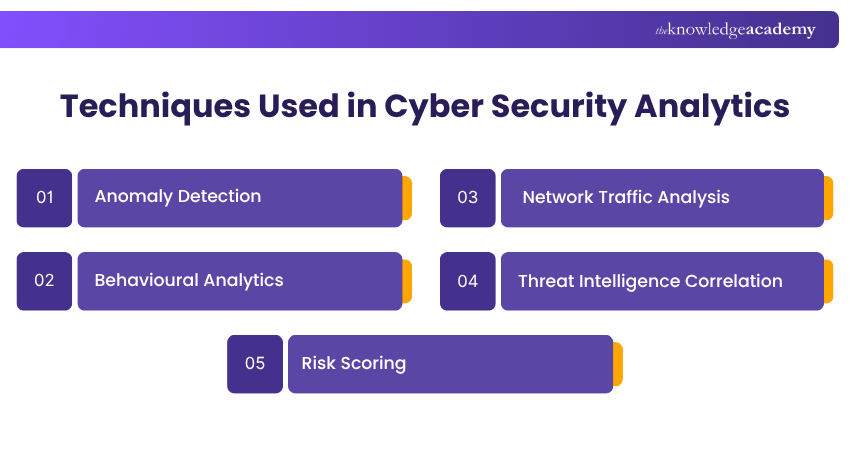
5 Techniques Used in Cyber Security Analytics
Cyber security analytics relies on several analytical techniques, each designed to surface a different kind of threat signal. Here are five techniques commonly used by security teams:
1) Anomaly Detection
Anomaly detection compares live activity, such as network traffic, system logs and user actions, against an established baseline of normal behaviour. Anything that deviates sharply from that baseline is flagged for review, because unusual activity can point to a potential attack.
This makes it useful for spotting threats with no known signature, including new malware variants and unfamiliar attack methods. Baselines need regular updating as systems and working patterns change, otherwise legitimate activity may trigger too many false alerts.
2) Behavioural Analytics
Behavioural analytics, often called User Behaviour Analytics (UBA) or Entity Behaviour Analytics (EBA), tracks the typical patterns of users and entities such as devices and servers. It builds a profile of what normal looks like for each one, then highlights activity that does not fit, such as a login at an unusual hour or a sudden spike in file access.
This helps catch compromised accounts, insider threats and lateral movement, where an attacker travels between systems after gaining initial access. Unlike broader anomaly detection, it focuses on who or what is acting rather than on overall traffic or log volumes, which gives security teams more context for investigation.
3) Network Traffic Analysis
Network traffic analysis captures and inspects the data packets moving across a network to understand what is communicating with what. Tools such as Wireshark and intrusion detection and prevention systems (IDS/IPS) help security teams examine this traffic in detail.
The aim is to spot malicious communications, for example data leaving the network for an unknown destination or devices contacting suspicious servers. Because it works at the network level, it can reveal threats that never appear in endpoint logs, although encrypted traffic can limit how much detail is visible.
4) Threat Intelligence Correlation
Threat intelligence correlation brings together external threat feeds, Indicators of Compromise (IOCs) and vulnerability databases. Internal alerts and activity are then cross-referenced against this information to see whether they match known attacker tactics, tools or infrastructure.
A match, such as a connection to an IP address already linked to malicious activity, can quickly raise an alert's priority. The technique is only as useful as the quality and freshness of the intelligence behind it, so feeds need to be reliable and regularly updated.
5) Risk Scoring
Risk scoring assigns dynamic risk values to users, assets or events based on how severe their behaviour or vulnerability level is. These scores change as new information arrives, for instance when a user triggers several suspicious alerts in a short period.
Security teams can then rank threats and focus on the highest-risk items first instead of working through every alert in order. This helps manage alert volume, although the scoring model should be reviewed regularly so it reflects the organisation's actual priorities.
Gain practical skills in using AI tools to strengthen cyber security solutions with our Generative AI in Cybersecurity Training Course - Sign up now!
How Does Cyber Security Analytics Work?
Cyber security analytics continuously monitors and analyses security data to identify suspicious activity and potential threats. A typical process includes:
1) Collect Security Data: Gather information from endpoints, users, applications, network devices, and event logs.
2) Analyse and Correlate Data: Normalise and analyse security data to identify patterns, anomalies, and suspicious activity.
3) Investigate and Respond: Prioritise detected threats and provide security teams with context to investigate and respond.
Trainer's Pro Tip
Review security data in context rather than relying on a single alert. Comparing activity across users, devices, and collected data can help teams assess threat severity and prioritise response.
How Businesses Use Cyber Security Analytics?
Businesses use cyber security analytics to monitor security activity across users, endpoints, applications, and networks. By bringing security data together, organisations can identify unusual behaviour, correlate related events, and investigate suspicious activity more effectively.
Security teams can also use analytics to review previous incidents, understand how threats developed, and identify patterns that may indicate recurring risks. This supports more informed investigation and helps organisations strengthen their security controls.
Cyber security analytics can also support security performance monitoring by helping teams track alerts, incident patterns, and areas that require further attention.
Strengthen cyber security analytics skills to identify suspicious patterns and detect fraud with our Fraud Analytics Training Course -Sign up now!
Benefits of Cyber Security Analytics
Let’s take a look at some of the benefits of using security analytics:
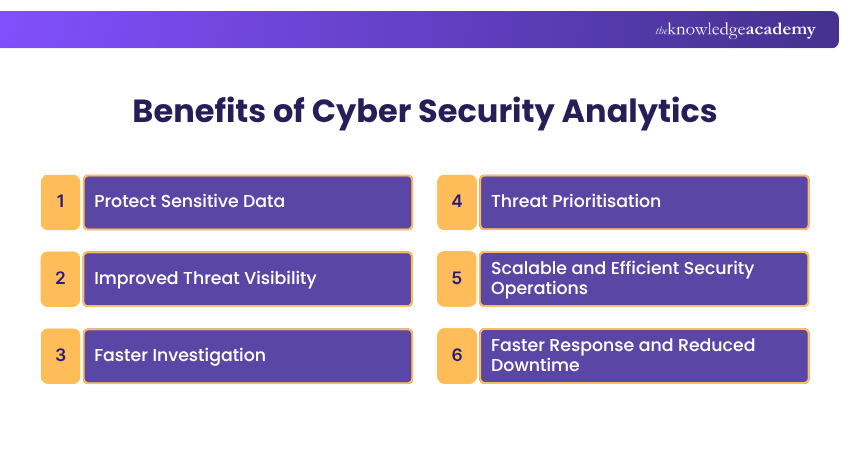
1) Protect Sensitive Data: Security analytics can identify unusual behaviour and suspicious activity earlier, helping organisations protect sensitive data and reduce the risk of data loss.
2) Improved Threat Visibility: Security analytics correlates information from multiple sources to provide broader visibility into suspicious activity.
3) Faster Investigation: Centralised security data can help teams investigate alerts and incidents more efficiently.
4) Threat Prioritisation: Security analytics can help teams rank alerts by severity, context and potential impact so higher-risk threats receive attention first.
5) Scalable and Efficient Security Operations: Automation and machine learning can help analyse large volumes of security data and identify anomalies faster, while reducing repetitive manual analysis for security teams.
6) Faster Response and Reduced Downtime: Better threat context and automated workflows can help security teams respond to incidents more quickly, reducing the duration and impact of incidents and helping organisations maintain operations.
Build the skills to detect threats, manage risks, and strengthen digital defence with our Certified Cyber Security Professional (CCS-PRO) – Sign up now!
Nilotpal Sarmah is a Senior Content Writer with 11+ years of overall experience spanning engineering, operations and content development. His technical knowledge and extensive writing experience enable him to simplify specialised topics across IT and Tech, Business Skills, Project Management, Health and Safety, and ISO and Compliance.
View Detail

 If you wish to make any changes to your course, please


