


We may not have the course you’re looking for. If you enquire or give us a call on 01344203999 and speak to our training experts, we may still be able to help with your training requirements.
Cyber Security Strategy: A Complete Guide
ByVishnu SankarLast updated on: 03 October 2026
Are you looking for strategies to secure your organisation from cyber security risks? Read this blog on cyber security strategies to secure your organisation.
Quick Look
1. A cyber security strategy connects security priorities with organisational objectives and risks.2. Identifying critical assets and data helps organisations focus protection where it matters most.3. Effective strategies combine people, processes, policies and technology.4. Incident response and recovery measures complement preventive security controls.5. Cyber security strategies should be reviewed as threats, technologies and organisational needs change.
Organisations worldwide are experiencing a sudden rise in cyber attacks; making it a necessity to implement an effective security strategy. Cyber attacks can pose several threats to businesses of any size or scale. Because of cyber attacks, many companies encounter financial losses and fail to comply with legal or regulatory requirements.
This even leads to the shutting down of their operations altogether. Cyber security works as a shield against a data breach or cyber attack for your business. To understand these security strategies, let’s explore the key concepts discussed in this blog.
What is a Cyber Security Strategy?
A cyber security strategy is a structured approach to protecting an organisation’s systems, data, and operations from cyber threats. It outlines security priorities, risk management measures, responsibilities, and controls based on the organisation’s objectives and risk environment. A well-defined strategy also supports effective detection, response, recovery, and ongoing improvement.
As cyber threats and business requirements change, the strategy should be reviewed and updated regularly. This helps organisations maintain appropriate protection while strengthening their ability to detect, respond to, and recover from security incidents.
Importance of Cyber Security Strategy
Are you wondering how cyber security will help you in the long run, or is it worth spending on cyber security? Then it’s time to understand the benefits of implementing cyber security strategies:
1) Improves the Safety of Personal Data
An organisation’s day-to-day operation revolves around user data or any other data generated daily. However, massive digitisation exposes this data to cyber criminals, industrial spies, and hackers. A sudden cyber attack can harm the privacy of employees, organisations, and customers.
Cyber security minimises the risks of internal threats, whether intentional or accidental. Intentional attacks are usually carried out by former employees, related partners, or third-party suppliers. But with proper cyber security strategies in place, employees don’t have to worry about data breaches.
2) Improves Business Goodwill
The goal of an organisation is to attract more consumers and improve brand loyalty. Data breaches can harm the organisation’s overall goodwill. While most reputed organisations work hard to retain consumers, organisations that encounter cyber security breaches often fall behind. Therefore, good security strategies will help any organisation improve their goodwill.
3) Boosts Productivity
Innovation in technologies is helping cybercriminals to come up with new strategies for data breaches and data attacks. Malware attacks can negatively impact the productivity, network, workflow, and even the overall functioning of an organisation. Consequently, it will force businesses to halt their operations for a long time.
A sound strategy with automated backups, virus scanning techniques, and enhanced firewalls will help organisations stay ahead of the hackers. This aims to educate employees on suspicious activities, scams, and email phishing, which in turn can boost productivity.
4) Safeguards Employees
An organisation’s workforce should be aware of threats arising from spyware, ransomware and data breaches. Cyber security creates a layer of protection for the organisation’s everyday operations. Thus, employees should be prevented from clicking on any harmful links or unknown files.
Employees should be trained to devise a successful response or take immediate action whenever a cyber threat occurs. Consequently, it will eliminate any errors or wastage of time. After ensuring the implementation of this stage, the organisation’s employees will no longer have to reach out to IT professionals to check if their actions comply with the organisation’s norms.
5) Reduces Website Crashes
Cyber security strategies can help protect websites and online services from threats that may disrupt their availability. Measures such as secure configurations, vulnerability management, monitoring, and DDoS protection can reduce the risk of security-related downtime.
Maintaining backups and recovery procedures can also help organisations restore affected services after an incident. This supports website availability and helps minimise disruptions to customers and business operations.
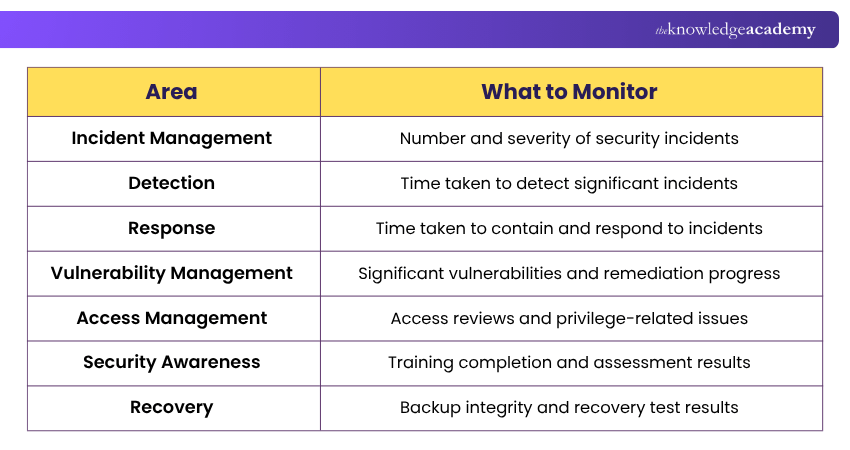
Here's a quick look at what to look into and what to monitor:
How to Develop a Cyber Security Strategy?
Building an effective cyber security strategy requires a logical and structured process. Activities such as risk assessment, data classification, asset mapping, framework selection, policy development and monitoring should work together to address organisational security priorities. Here are the ways to develop it:
1) Understand Organisational Objectives
Begin with the organisation rather than its security tools. Identify:
a) Critical business operations
b) Important services
c) Strategic objectives
d) Regulatory obligations
e) Key stakeholders
f) Dependencies on technology and third parties
Security priorities should support these wider organisational needs.
2) Identify Critical Assets and Data
Create and maintain an inventory of important systems, applications, devices, information and services. Asset mapping and detailed records can help organisations understand what they need to protect and where critical resources are located. Classify information according to its sensitivity and importance so that appropriate protection can be prioritised.
3) Assess Cyber Risks
Identify threats, vulnerabilities and potential impacts affecting critical assets. Risk assessment helps determine which risks require immediate attention and which can be addressed through longer-term improvements.
Your best defence starts with awareness! Learn how to identify common cyber risks with the Cyber Security Awareness Training – Sign up now!
4) Define Security Priorities
Not every risk can be addressed at the same time. Prioritise security activities according to factors such as:
a) Risk severity
b) Business impact
c) Criticality of affected assets
d) Regulatory requirements
e) Available resources
This helps turn risk assessment findings into actionable priorities.
5) Select an Appropriate Security Framework
A cyber security framework helps organisations structure their security activities and manage risks. Examples include NIST CSF 2.0 and ISO/IEC 27001:2022, which serve different purposes. Organisations should choose an approach based on their objectives, risks, regulatory requirements, and available resources.
6) Establish Policies and Responsibilities
Define the policies, responsibilities and decision-making processes required to support the strategy. Security should involve appropriate collaboration between management, employees, IT teams, data owners and relevant third parties. Clear communication helps you make sure everyone understands their responsibilities.
Trainer’s Insight
Every major security responsibility should have a clear owner. Define who manages risks, approves policies, responds to incidents and communicates security issues so responsibilities remain clear when action is required.
7) Implement Security Controls
Select controls according to identified risks. Depending on organisational needs, controls may include:
a) Access restrictions
b) Authentication measures
c) Security monitoring
d) Vulnerability management
e) Backups
f) Network protection
g) Automated scanning
h) Security awareness measures
A layered approach helps avoid relying on a single protective measure.
8) Prepare Incident Response and Recovery Plans
Even strong preventive controls cannot guarantee that incidents will never occur. Establish how the organisation will detect, contain, communicate, recover from and learn from cyber security incidents. Recovery arrangements should also consider how critical business operations will continue or be restored.
9) Monitor, Review and Improve the Strategy
Cyber security risks do not remain static. Review the strategy as technologies, suppliers, business operations and significant risks change. Security policies, controls and response plans should also be reviewed regularly to make sure they remain appropriate and effective.
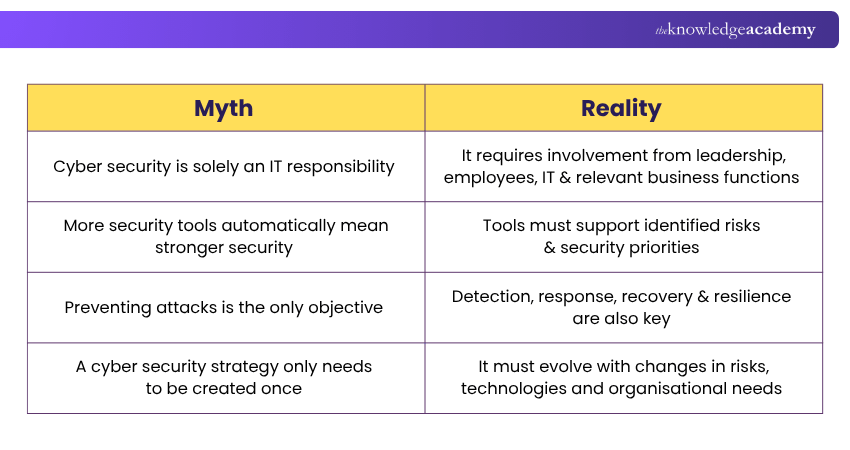
Here are some myths related to cyber security strategy you need to watch out for:
Factors Affecting Cyber Security Strategy
Several internal and external factors can influence how an organisation develops and maintains its cyber security strategy. Here are the key factors to consider:
a) Organisational Objectives: Security priorities should align with business goals and critical operations. This helps ensure security measures support organisational needs.
b) Risk Exposure: The nature and severity of cyber risks affect security priorities. Organisations should focus resources on their most significant risks.
c) Regulatory Requirements: Applicable laws, regulations, and industry requirements influence security decisions. Organisations must ensure their practices meet relevant obligations.
d) Technology Environment: Cloud services, networks, applications, and emerging technologies affect security requirements. Strategies should address risks associated with the organisation’s technology landscape.
e) Available Resources: Budget, skills, personnel, and security capabilities can influence implementation. Organisations should prioritise measures that can be effectively supported.
f) Third-Party Dependencies: Suppliers and service providers can introduce additional cyber security risks. Strategies should account for supplier security, access, and dependencies.
Common Cyber Security Strategy Mistakes
Common mistakes include:1. Treating cyber security solely as an IT responsibility2. Buying security tools before understanding business risks3. Failing to maintain an accurate asset inventory4. Leaving security responsibilities unclear5. Giving users more access than required6. Ignoring third-party risks7. Focusing entirely on prevention while neglecting response and recovery8. Failing to measure whether controls are effective9. Allowing the strategy to become outdated
Develop a proactive approach to protecting systems, data and operations with the Cyber Security Risk Management Course – Sign up now!
Vishnu Sankar is a Senior Content Writer with 5+ years of experience across content development, software development, web development and system administration. His technical background and professional training support his expertise in IT and Tech, while his extensive research and writing experience covers Project Management and Health and Safety.
View Detail

 If you wish to make any changes to your course, please


