


We may not have the course you’re looking for. If you enquire or give us a call on +44 1344 203 999 and speak to our training experts, we may still be able to help with your training requirements.
What are the Top 8 CISSP Domains?
ByJyoti TuraLast updated on: 03 October 2026
The eight CISSP domains are security & risk management, asset security, security architecture, network security, identity management, security testing, security operations, and software development security. They align security controls with business objectives and regulatory expectations. Overall, they help protect the confidentiality, integrity, and availability of information.
What’s Inside This Blog
1. What CISSP is and why its eight domains matter2. A breakdown of all eight CISSP domains and what each one covers3. CISSP domain weightage and how it relates to the exam4. Experience requirements and key CISSP exam details5. Which CISSP domains may require more preparation depending on your background
So, you’ve decided to dive into the world of CISSP? Good choice! Think of it as the master plan for cybersecurity professionals. At its core lies a powerful framework that covers key areas of modern information security.
CISSP domains are like puzzle pieces that, when put together, give you a 360-degree view of modern security practices. Whether you're starting your journey or want a refresher, understanding these domains is a gamechanger. Let’s explore the terrain and see how each piece fits into the big picture of cyber defence.
Quick Check
Which area are you already most familiar with?A. Security governance and riskB. Architecture and network securityC. Identity, access and security testingD. Security operations and software security
Keep your answer in mind as you explore the eight CISSP domains. The areas outside your existing experience may require additional attention during preparation.
What is CISSP?
Certified Information Systems Security Professional (CISSP) is a globally recognised certification offered by the International Information System Security Certification Consortium (ISC2). It validates that a professional has the knowledge and practical understanding required to design, implement, and manage an organisation’s information security frameworks effectively.
With the help of CISSP, individuals demonstrate their ability to handle security challenges, support compliance requirements, and protect organisational data against evolving cyber threats. It encourages professionals to follow best practices and ethical standards in protecting information assets.
The 8 CISSP Domains Explained
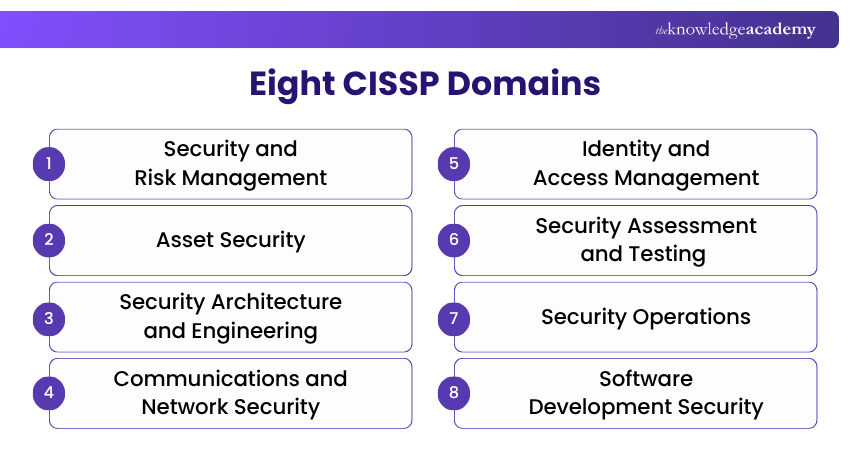
The CISSP certification is structured around eight core domains that together form a complete foundation of cybersecurity knowledge. Each domain focuses on a different aspect of protecting information. Candidates are assessed across all eight CISSP domains. Let us understand the CISSP eight domains in depth:
1) Security and Risk Management
This CISSP domain forms the foundation and provides an overview of the key principles of information systems security management. The CISSP exam typically allocates 16% weight to this domain. It comprises the following:
1) Understand professional ethics
2) Security governance principles and concepts
3) Compliance and other requirements
4) Understanding legal and regulatory issues in the context of information security
5) Personnel security policies and procedures
6) Risk-based management concepts
2) Asset Security
This CISSP domain focuses on data protection, management, and safety controls. The content derived from this domain accounts for approximately 10% of the CISSP exam. It encompasses the responsibilities associated with various roles in data management, information ownership and processing, privacy concerns, and limitations. It includes the following:
1) Data lifecycle management
2) Data security controls
3) Information and asset retention
4) Compliance requirements
Arm yourself with expertise - Register for the Chief Information Security Officer Training today!
3) Security Architecture and Engineering
Security architecture and engineering accounts for 13% of the CISSP exam. This domain deals with designing and building secure systems. Professionals understand how security models, encryption methods, and trusted computing principles are used to create resilient and reliable infrastructures. This domain covers:
1) Research, implement and manage engineering processes using secure design principles
2) Understanding the fundamental concepts of security models
3) Understanding security capabilities and controls based on security requirements
4) Assessing and mitigating vulnerabilities in security systems
5) Assessing and mitigating vulnerabilities in cryptographic systems
6) Designing and facilitating security controls
Trainer's Insight
Security architecture and engineering covers several technical concepts, so avoid treating them as isolated terms. Try connecting each concept to three questions: What needs protection? What could compromise it? Which security design or control can reduce the risk?
4) Communications and Network Security
This CISSP domain focuses on designing and securing network architectures, communication channels and network components. It includes about 13% of the content for the CISSP exam. It covers secure network design principles and methods for protecting network components and communication channels.
The questions on communication networks, diverse network design characteristics, media transmission, and wireless communications will be presented to the candidates appearing in the exam. Communications and network security includes
1) Assessing and implementing secure design principles
2) Protecting network components
3) Methods to implement secure communication channels
5) Identity and Access Management
The identity and access management domain includes about 13% of the content in the CISSP exam. This domain aids information security professionals in better understanding how to limit users' access to data. It comprises the following:
1) Methods to control physical and logical access to assets
2) Identification and authentication of people, devices, and services.
3) Centralised third-party identification service
4) Implement authentication systems
5) Identity and access provisioning lifecycle
6) Security Assessment and Testing
This CISSP domain covers the methods and tools used to evaluate the security of processes and identify flaws in design or code, as well as potential vulnerabilities. It also includes techniques such as vulnerability assessments and penetration testing to detect risks. This domain comprises 12% of the CISSP exam. It focuses on:
1) Designing and validating assessment, test and audit strategies
2) Conducting security control testing
3) Collecting security process data
4) Analysing test outputs and generating reports
5) Conducting or facilitating security audits
7) Security Operations
Security operations deal with the everyday protection and monitoring of IT environments. It includes incident response, logging, monitoring, disaster recovery, and backup management. You can learn how to detect attacks quickly and respond effectively to minimise damage. This domain comprises 13% of the exam modules. It covers:
1) Understand and abide by the investigations
2) Configuration management
3) Logging and monitoring activities
4) Securing resources
5) Vulnerability management
6) Apply foundational security operations concepts
7) Applying resource protection techniques
8) Conduct incident management
9) Implement and test a disaster recovery
10) Manage and implement personnel safety and security
11) Plan business continuity
8) Software Development Security
Software development security focuses on integrating security throughout the Software Development Life Cycle (SDLC) and assessing the effectiveness of software security. It accounts for an average of 10% of the CISSP exam. Software development security comprises the following:
1) Security integration in the Software Development Life Cycle (SDLC)
2) Detect and apply security controls
3) Assessing software's security impact
4) Apply secure coding guidelines and standards
Enhance your cybersecurity skills with the ISSMP Training - Join now!
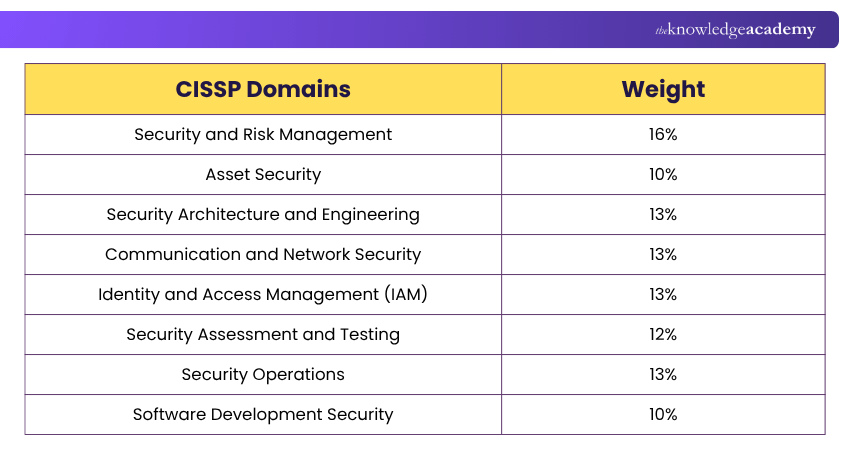
CISSP Domain List and Examination Weights Across
Here is a table explaining the CISSP domain list along with their examination weightage:
Bonus Tip
Don’t use exam weightage as the only way to prioritise your study time. A domain with a lower weight may need more attention if it is unfamiliar to you, while a higher-weight domain may require less revision if it already matches your professional experience.
CISSP Experience Requirements and Exam Details
If you're aiming to become a CISSP-certified professional, here’s what you need to know about the eligibility and exam format.
1) CISSP Experience Requirements
To apply for the CISSP exam, you must have at least five years of cumulative, full-time work experience in information security. Your experience should cover at least two or more of the eight CISSP domains.
However, you can reduce the work experience requirement by one year if you meet any one of the following conditions:
1) You’ve completed a post-secondary degree, such as a bachelor's or master's degree in computer science, Information Technology (IT) or related fields.
2) You hold an approved credential from the ISC2 approved list.
3) Relevant part-time work and internships can be counted toward fulfilling the experience requirement.
2) Examination Plan of Action
The CISSP exam is a Computerised Adaptive Testing (CAT) that evaluates both theoretical knowledge and practical decision-making skills across all eight domains. You can prepare an effective study plan by clearly understanding the nature of the exam. Key exam details include:
1) Exam Duration: 3 hours
2) Number of Questions: 100 to 150 questions
3) Question Format: Multiple-choice and advanced question types
4) Passing Score: 700 out of 1000 points
5) Languages Available: English, Chinese, German, Japanese, and Spanish
Test Your Understanding
Can you match each security activity to the correct CISSP Domain?A. Managing user authentication and access permissionsB. Conducting security audits and control testingC. Planning incident response and disaster recoveryD. Integrating security into the SDLCAnswers:A — Identity and Access ManagementB — Security Assessment and TestingC — Security OperationsD — Software Development Security
What is the Hardest CISSP Domain?
No domain in the CISSP exam is inherently the hardest, as the level of difficulty mainly varies based on a candidate’s background and experience. However, some may find security architecture and engineering and software development security the most challenging.
This is due to the reason that they include technical concepts such as cryptography, security models, hardware security, secure coding practices, testing methods, and the secure Software Development Lifecycle (SDLC). It requires both theoretical understanding and the ability to apply security controls in real-world architectures.
Prepare for CISSP and advance your cybersecurity career with the CISSP Courses now!

Jyoti Tura is a Senior Web & UX/UI Manager with 7+ years of experience in front-end development, web development and user-focused interface design. Her technical expertise and managerial responsibilities support her knowledge across IT and Tech, Leadership and Management.
View Detail

 If you wish to make any changes to your course, please


