


We may not have the course you’re looking for. If you enquire or give us a call on 01344203999 and speak to our training experts, we may still be able to help with your training requirements.
Top 8 Types of Cyber Security - A Comprehensive Guide
ByNilotpal SarmahLast updated on: 10 October 2026
Cyber security protects computers, networks, systems, and data from cyber threats, unauthorised access, disruption, and damage. This blog explores the top eight types of cyber security, including network, cloud, endpoint, application, internet, information, mobile security, and IAM. It highlights their roles in maintaining a secure digital environment.
Key Highlights
1. No single security control can protect every part of a digital environment.2. Cloud environments require security responsibilities to be understood by both providers and customers.3. Endpoint and application security address risks at different points across devices and software.4. IAM helps ensure that access to organisational resources is granted to appropriate users.5. Effective cyber security depends on combining relevant controls based on systems, information and risks.
In our increasingly connected world, safeguarding your online presence has never been more important. Cyber security protects computers, networks, and data from cyber threats. This blog discusses the different types of cyber security that help keep our digital lives secure. Understanding these types can empower you to better protect your information and stay safe online.
Cybercrime continues to create substantial financial risks worldwide, highlighting the growing importance of effective cyber security measures. From network security to mobile security, each type plays a key role in defending against attacks. Explore how these essential cyber security measures can make a difference in your digital security strategy.
What is Cyber Security?
Cyber security is the practice of safeguarding computers, networks, and data from unauthorised access or attacks. It helps protect the confidentiality, integrity and availability of information and systems. Cyber security uses various tools and techniques, such as firewalls and encryption, to prevent, detect and respond to cyber threats.
Cyber security aims to protect digital systems and information from threats. By implementing appropriate security measures, individuals and organisations can reduce the risk of data breaches, cyber attacks and other security incidents.
What are the Types of Cyber Security?
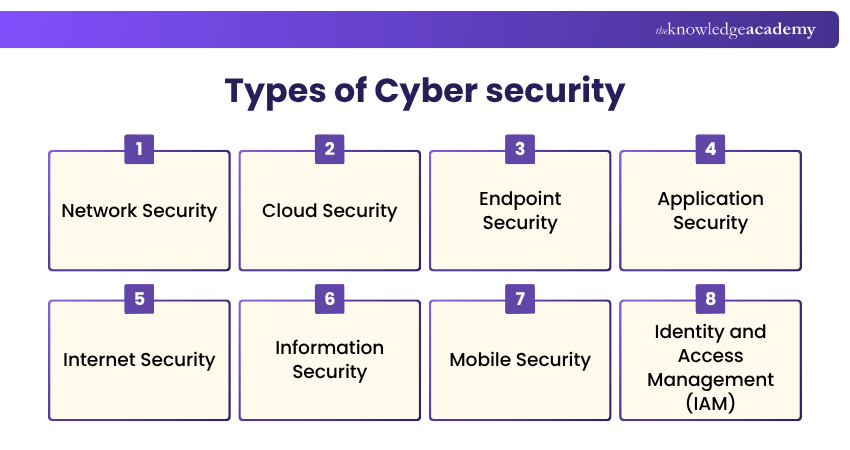
Here are some of the common types of cybersecurity:
1) Network Security
Network security protects networks, connected systems, and traffic from unauthorised access, misuse, disruption, and other cyber threats. This type of security ensures that your network's integrity, confidentiality, and availability are maintained. Key components include firewalls, Intrusion Detection Systems (IDS), and Intrusion Prevention Systems (IPS).
These tools monitor network traffic based on predetermined security rules. A strong network security framework can help prevent unauthorised access, misuse, modification and disruption of network resources.
2) Cloud Security
With the rise of cloud computing, securing data hosted in the cloud has become increasingly important. Cloud security involves policies, technologies, and controls designed to protect cloud data, applications, and infrastructure from threats.
Cloud service providers implement robust security measures, but users must also adopt best practices, such as using strong passwords, enabling Multi-factor Authentication (MFA), and regularly updating security settings. Data encryption, regular backups, and monitoring are also vital components of cloud security.
Trainer’s Pro Tip
Do not assume moving data or applications to the cloud transfers all security responsibility to the provider. Understand which security responsibilities belong to the provider and which remain with your organisation.
3) Endpoint Security
Endpoint security focuses on protecting end-user devices such as desktops, laptops, and mobile devices. These devices can provide entry points for cyber attacks, making their security crucial. This type of security involves using antivirus software, Endpoint Detection and Response (EDR) tools, and host-based firewalls to safeguard devices from malicious activities. Regular updates and patches are essential to fix vulnerabilities that could be exploited by cybercriminals.
4) Application Security
Application security refers to measures taken to protect software applications from vulnerabilities throughout their lifecycle, including design, development, deployment and maintenance. Security standards and secure development practices can help organisations identify and address application vulnerabilities.
Practices include code reviews, penetration testing, and the use of security tools to identify and fix vulnerabilities. Secure coding practices and regular updates are important to maintaining robust application security.
Learn best practices for password security, safe browsing, and data protection with our Cyber Security Awareness Training – Register now!
5) Internet Security
Internet security covers the measures taken to protect users and their data when using the internet. This includes safeguarding against threats such as malware, phishing attacks, and Denial-of-Service (DoS) attacks. Using secure web gateways, antivirus software, internet security suites, and VPNs (Virtual Private Networks) can enhance internet security.
Additionally, educating users about safe browsing practices, such as avoiding suspicious links and using strong passwords, plays a significant role in preventing internet-based threats.
6) Information Security
Information security, also known as InfoSec, focuses on protecting the confidentiality, integrity and availability of information. This helps ensure that information is protected from unauthorised access or disclosure, safeguarded against improper modification and available to authorised users when needed.
Key components of information security include data encryption, access controls, and data masking. Regular audits and compliance with security standards and regulations are also crucial to maintaining information security. Together, confidentiality, integrity and availability form the CIA triad, a foundational model for information security.
7) Mobile Security
As mobile device usage continues to grow, mobile security has become an important aspect of cyber security. This type of security involves protecting mobile devices and the data they store from threats such as malware, unauthorised access, and data breaches.
Practices include using Mobile Device Management (MDM) solutions, securing mobile applications, and implementing encryption and strong authentication methods. Users should also be encouraged to update their devices regularly and download apps from trusted sources only.
8) Identity and Access Management (IAM)
Identity and Access Management (IAM) involves managing digital identities and controlling their access to resources within an organisation. IAM helps ensure that users and systems receive appropriate access to resources based on defined identities, permissions, roles, and security policies.
IAM practices include user provisioning and de-provisioning, Role-based Access Control (RBAC), and MFA. Implementing a robust IAM framework helps organisations streamline user access, enhance security, and comply with regulatory requirements.
Quick Cyber Security Review
Check whether your organisation:
1. Protects networks and endpoints with appropriate controls2. Reviews user identities and access permissions3. Applies security throughout the application lifecycle4. Understands responsibilities for securing cloud environments5. Protects sensitive information based on its risk and value6. Keeps devices, applications and systems updated7. Regularly reviews controls as systems and risks change
Learn global security standards and compliance with our Cyber Security Risk Management Training – Join now!
Nilotpal Sarmah is a Senior Content Writer with 11+ years of overall experience spanning engineering, operations and content development. His technical knowledge and extensive writing experience enable him to simplify specialised topics across IT and Tech, Business Skills, Project Management, Health and Safety, and ISO and Compliance.
View Detail

 If you wish to make any changes to your course, please


