



We may not have the course you’re looking for. If you enquire or give us a call on 01344203999 and speak to our training experts, we may still be able to help with your training requirements.
What is Vendor Risk Management: A Detailed Guide
ByDavid EvansLast updated on: 08 October 2026
Curious about how to protect your business from external risks? Discover vendor risk management, a strategic approach used by various organisations. Read this blog to learn how to identify, evaluate, and minimise the risks of working with third-party vendors through effective vendor risk management practices.
What You Should Know
1. Vendor risk management helps identify and manage risks arising from third-party relationships.2. Vendor risks can include cyber security, operational, financial, compliance, reputational and business continuity risks.3. Vendors should be assessed in proportion to their risk and criticality, so higher-risk vendors receive closer scrutiny than lower-risk ones.4. Effective VRM covers the complete relationship, from initial assessment and contracting to monitoring and offboarding.5. Continuous monitoring helps organisations respond when vendor performance, circumstances or risk exposure changes.
Organisations rely on suppliers, service providers and other third parties for everything from cloud hosting to payroll, and each relationship brings risks that the organisation does not directly control. Vendor Risk Management (VRM) is the practice of evaluating the risk profile of these partners both before and during a contract, so that problems are addressed before they affect the business.
Applied across the entire vendor lifecycle, including offboarding, VRM helps keep disruption, financial impact and reputational damage to a minimum. A robust programme turns vendor relationships from a source of uncertainty into something that supports smooth and secure operations.
What is Vendor Risk Management?
Vendor Risk Management (VRM) is a strategic process that organisations use to identify, assess, and mitigate the risks associated with their third-party vendors, suppliers, and service providers. It’s an important part of an organisation’s overall risk management strategy and cyber security efforts.
The goal of VRM is to ensure that the organisation’s vendors do not pose a threat to its financial, operational, reputational, or cyber security posture. By effectively managing risks, organisations can maintain robust security practices and foster strong, secure, and mutually beneficial relationships with their vendors.
Why is Vendor Risk Management Important?
Vendors often have access to an organisation's data, systems and customers, so a weakness in one vendor can quickly become a problem for the organisation itself. Vendor Risk Management (VRM) helps organisations reduce the chance of this happening by checking how vendors handle security, compliance and reliability before and during a contract.
The cost of not managing vendor risk can be significant. A vendor data breach can expose sensitive information, a service outage can halt operations, and a compliance failure can lead to fines or damage to reputation. Because these problems can start outside the organisation but still land on it, VRM is a core part of protecting data, keeping services running and maintaining trust with customers and regulators.
Who is Considered a Vendor?
A vendor can be any external party that supplies goods, services or technology to an organisation. This can include:
1. Suppliers2. Service providers3. Contractors4. Technology providers5. Outsourced service providers
Vendor Risk Management Lifecycle
A well-structured Vendor Risk Management (VRM) strategy should cover the entire vendor relationship period. Organisations can effectively manage and prevent risks by systematically addressing the various phases of the vendor lifecycle. Let's explore the key steps involved in the vendor risk management lifecycle:
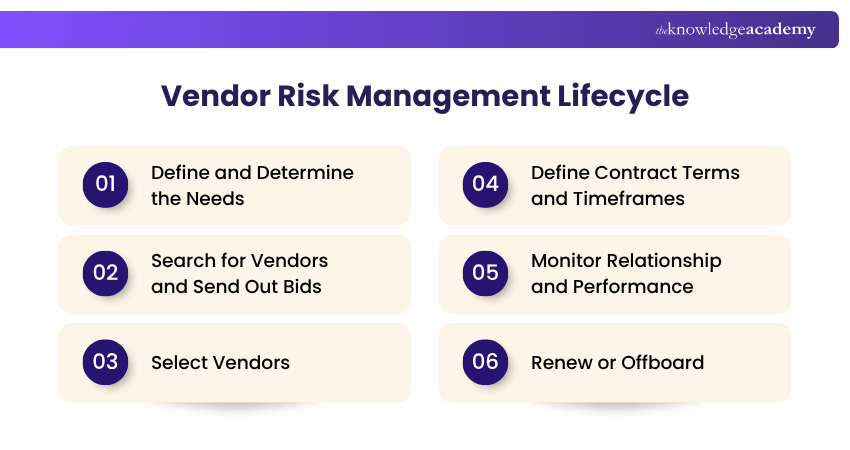
1) Define and Determine the Needs
The vendor risk management lifecycle starts precisely when the organisation has clarified all its needs and wants. This entails the identification of the specific products or services that the company needs to procure from vendors.
2) Search for Vendors and Send Out Bids
Companies need to establish criteria for selecting the best service providers and then hire them. Strategies for this process include seeking referrals, conducting industry research, and issuing Requests for Proposals (RFPs). A well-written RFP states the organisation's requirements and risk expectations up front, so bidders can develop proposals that address them.
3) Select Vendors
Procurement management involves comparing quotations or proposals provided by vendors that meet organisational needs. Reviewing vendor ratings, checking references and carrying out background checks are central to making sound decisions when selecting vendors. This ensures they align with all organisational requirements.
4) Define Contract Terms and Timeframes
Vendor selection is followed by negotiating contract terms and setting deadlines. Transparent contracts that clearly outline a vendor's responsibilities, deliverables, performance parameters, risk management, data protection, confidentiality, and dispute resolution are essential. Ensuring alignment on language and timelines is crucial to avoiding disputes and misunderstandings.
Pro Tip
Include exit requirements during contracting rather than waiting until termination. Clear provisions for data return or deletion, access removal and service transition can make vendor offboarding safer and smoother.
5) Monitor Relationship and Performance
Vendor risk management encompasses more than just a set of activities involving vendor selection; it also includes overseeing the vendor’s performance and relationship with the client. This involves monitoring to ensure the fulfilment of contract requirements, provisions, service levels, and risk management methods.
6) Renew or Offboard
The final stage of the vendor lifecycle occurs at the point of contract renewal or termination. Organisations evaluate vendors based on their performance, risk mitigation and ability to respond to changing requirements. This assessment helps determine whether to renew, renegotiate or terminate the contract.
If the contract ends, offboarding should follow the exit terms agreed at the contracting stage, such as returning or deleting data, removing system access and transitioning the service to a new provider or in-house team.
Build the skills to identify and respond to risks before they disrupt your transformation goals with the Risk Management for Change Training – Sign up now!
Benefits of Vendor Risk Management
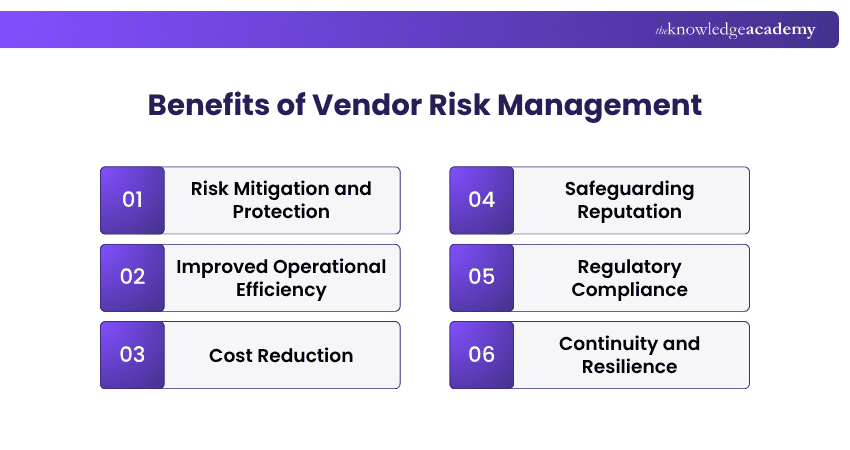
Implementing robust vendor risk management offers several significant benefits to organisations. Let's explore some of the key advantages:
1) Risk Mitigation and Protection
Good vendor risk management enables companies to address risk-related issues with vendors effectively. Through rigorous due diligence and assessment mechanisms, weaknesses are identified and resolved, reducing the number of disruptions, financial losses, legal issues, and reputational damage.
2) Improved Operational Efficiency
An efficient vendor risk management system ensures that vendors comply with the company's operational expectations and obligations. Continuous monitoring and evaluation help identify issues at an early stage, allowing timely resolution of complications with vendors.
3) Cost Reduction
Vendor risk management efforts enable companies to optimise costs through risk assessment and favourable terms and pricing structures. Quality management serves as a budget-saving tool by reducing the costs of unexpected failures from vendor issues or breaches, helping to keep expenditures under control.
4) Safeguarding Reputation
Vendors’ responses play a critical role in establishing an organisation’s reputation. Active vendor risk management not only safeguards reputation but also creates supportive environments that lead to the success of customers and stakeholders.
5) Regulatory Compliance
Comprehensive vendor risk management ensures that vendors comply with rules such as data privacy and anti-corruption. This minimises risks arising from regulations and unethical practices, demonstrating the company’s commitment to ethics.
6) Continuity and Resilience
Companies review suppliers' continuity plans to prevent interruptions. Identifying and addressing weaknesses helps decrease vulnerability to situations like technical glitches or natural disasters, thereby maintaining operational continuity.
See the risk and shape the response quickly and effectively. Learn how in the MoR® Management of Risk Training – Sign up now!
Quick Vendor Risk Checklist
Before approving a vendor, check:
□ What data or systems will the vendor access?□ How critical is the vendor to operations?□ Has its security posture been assessed?□ Are relevant compliance requirements addressed?□ Has financial and operational resilience been considered?□ Are risk responsibilities reflected in the contract?□ Are monitoring requirements defined?□ Is there an appropriate offboarding process?
David Evans creates accessible resources that help professionals understand different approaches to planning and delivering projects. His content addresses changing requirements, collaborative working and the practical demands of contemporary project environments.
View Detail

 If you wish to make any changes to your course, please


