SALE LIVE
SAVE UPTO 60% BLACK FRIDAY

ISO 27001 Training Black Friday Offers

ISO 27001 Training courses are part of our Black Friday sale. Lock in up to 60% off now, choose online, classroom or onsite training, and schedule your course any time through 2027. Group bookings save up to 60%.

Offer ends 27 November 2026

ISO 27001 Training

Online Instructor-led (1 days)

Online Self-paced (8 hours)

ISO 27001 Foundation Exam

ISO 27001 Foundation Course Outline

Module 1: Introduction to ISO 27001

  • Introduction
  • Compatibility with Other Management System Standards
  • ISO 27001:2022 and Its Clauses

Module 2: Information Security

  • What is Business?
  • Industries
  • Risk
  • SWOT Analysis
  • Constructs and Characteristics of Assets
  • Security and Privacy
  • Triad of Information Security
  • Cyber Security is Everyone’s Responsibility
  • Cybersecurity Landscape
  • What is Information Security?
  • Information Security Management
  • Need of Information Security
  • Threats to Information Security
  • Active and Passive Attacks

Module 3: Context of the Organisation

  • Understanding the Organisation and Its Context
  • Understanding the Needs and Expectations of Interested Parties
  • Determining the Scope of the Information Security Management System
  • Information Security Management System

Module 4: Leadership

  • Leadership and Commitment
  • Policy
  • Organisational Roles, Responsibilities, and Authorities

Module 5: Planning

  • Organisational Roles, Responsibilities, and Authorities
  • Information Security Objectives and Planning to Achieve Them
  • Planning of Changes

Module 6: Support

  • Resources
  • Competence
  • Awareness
  • Communication
  • Documented Information

Module 7: Operation

  • Operational Planning and Control
  • Information Security Risk Assessment
  • Information Security Risk Treatment
  • Drafting Reports and Test Plans

Show moredown

Who Should Attend this ISO 27001 Foundation Course?

Our ISO 27001 Foundation Course is designed for professionals seeking to build foundational knowledge of information security management and ISO/IEC 27001 requirements. The following professionals can benefit from this course:

  • Information Security Officers
  • Cybersecurity Professionals
  • Risk Managers
  • Compliance Officers
  • Auditors
  • IT Professionals
  • Administrative Professionals

Prerequisites for the ISO 27001 Foundation Course

There are no formal prerequisites to attend this ISO 27001 Foundation Course. However, familiarity with Information Security principles can be beneficial for the delegates.

ISO 27001 Foundation Course Overview

The ISO 27001 Foundation Training introduces the principles of Information Security Management and ISO 27001. It explains how an Information Security Management System (ISMS) helps organisations manage information security risks and protect valuable information.

Delegates will develop knowledge of information security, risk assessment audit, risk treatment, ISMS requirements, and documented information. They will also understand organisational context, leadership, planning, support, and operational controls.

This 1-Day course by The Knowledge Academy enables delegates to apply foundational ISO 27001 knowledge within workplace settings. They will be able to support ISMS activities, contribute to risk management, and strengthen organisational information security practices.

ISO 27001 Foundation Training Course Objectives

  • To introduce the concept of information security management and the benefits of an ISMS
  • To understand the ISO 27001 standard's requirements and its application within an organisation
  • To grasp the process approach to establishing, implementing, operating, monitoring, reviewing, maintaining, and improving an ISMS
  • To recognise the significance of legal, regulatory, and contractual requirements in managing information security
  • To learn the key terms, definitions, and principles of information security management according to ISO 27001
  • To develop an understanding of information security risk assessment and risk treatment within an ISMS

Learning Outcomes of this ISO 27001 Foundation Course

Upon completing this ISO 27001 Foundation Course, delegates will be able to explain the key requirements of ISO 27001:2022 and the purpose of an Information Security Management System (ISMS). They will also be able to support risk assessment and treatment activities, understand organisational responsibilities, and contribute to planning, documentation, and operational information security practices.

Benefits of Completing this ISO 27001 Foundation Course

Completing this course develops essential knowledge of information security management and the principles of an Information Security Management System (ISMS). Key benefits include:

  • ISMS Knowledge: Understand the structure, purpose, and key requirements of an Information Security Management System.
  • Risk Management Skills: Develop knowledge of information security risk assessment, risk treatment, and operational controls.
  • Information Security Awareness: Understand common information security threats, security principles, and the importance of protecting organisational assets.
  • ISO 27001 Understanding: Build familiarity with ISO 27001 clauses and their role within information security management.
  • Organisational Support: Understand leadership responsibilities, resources, competence, communication, and documented information within an ISMS.
  • Professional Development: Build foundational knowledge for progressing into information security management and ISO 27001-related responsibilities.

Career Opportunities After Completing this ISO 27001 Foundation Course

Our ISO 27001 Foundation Course develops essential knowledge of information security management principles and ISO/IEC 27001 requirements, supporting career development in information security and compliance. Combined with relevant experience and additional qualifications, this knowledge can help professionals pursue the following career opportunities:

  • Information Security Analyst: Support information security activities by identifying risks, threats, and requirements within an organisation.
  • ISMS Coordinator: Assist with the operation, documentation, and ongoing support of an organisation's Information Security Management System.
  • Information Security Officer: Support organisational security practices, audit policies, risk assessments, and information protection activities.
  • Risk Analyst: Help identify and assess information security risks and support appropriate risk treatment activities.
  • Compliance Coordinator: Support organisational processes and documented information associated with information security requirements.
  • Information Security Manager: With further experience and development, progress towards managing information security practices, responsibilities, and ISMS activities.

Show moredown

What’s Included in this ISO 27001 Foundation Training Course?

  • ISO 27001 Foundation Examination
  • World-Class Training Sessions from Experienced Instructors
  • Interactive Learning with 24*7 Support
  • Digital Delegate Pack

Show moredown

ISO 27001 Foundation Exam Information

To achieve the ISO 27001 Foundation, candidates will need to sit for an examination. The exam format is as follows: 

  • Question Type: Multiple Choice 
  • Total Questions: 30 
  • Total Marks: 30 Marks 
  • Pass Mark: 50%, or 15/30 Marks 
  • Duration: 40 Minutes
  • Open Book/ Closed Book: Closed Book

Show moredown

Online Instructor-led (5 days)

Online Self-paced (40 hours)

ISO 27001 Lead Auditor Exam

ISO 27001 Lead Auditor Course Outline

Module 1: Introduction to ISO 27001

  • Introduction
  • Compatibility with Other Management System Standards
  • ISO 27001:2022 and its Clauses

Module 2: Information Security

  • What is Business?
  • Industries
  • Risk
  • SWOT Analysis
  • Constructs and Characteristics of Assets
  • Security and Privacy
  • Triad of Information Security
  • Cyber Security is Everyone’s Responsibility
  • Cybersecurity Landscape
  • What is Information Security?
  • Information Security Management
  • Need of Information Security
  • Threats to Information Security
  • Active and Passive Attacks

Module 3: Context of the Organisation

  • Understanding the Organisation and Its Context
  • Understanding the Needs and Expectations of Interested Parties
  • Determining the Scope of the Information Security Management System
  • Information Security Management System

Module 4: Leadership

  • Leadership and Commitment
  • Policy
  • Organisational Roles, Responsibilities, and Authorities

Module 5: Planning

  • Actions to Address Risks and Opportunities
  • Information Security Objectives and Planning to Achieve Them
  • Planning of Changes

Module 6: Support

  • Resources
  • Competence
  • Awareness
  • Communication
  • Documented Information

Module 7: Operation

  • Documented Information
  • Information Security Risk Assessment
  • Information Security Risk Treatment

Module 8: Performance Evaluation

  • Monitoring, Measurement, Analysis, and Evaluation
  • Internal Audit
  • Management Review

Module 9: Improvement

  • Nonconformity and Corrective Action
  • Continual Improvement

Module 10: Introduction to Auditing

  • Internal Audit Charter
  • Communicate with Organisation and Audit Committee
  • Auditing Reflects
  • General and Internal Auditing Standards and Guidance
  • Auditing Types
  • Auditing Techniques
  • Auditing Principles
  • Phases of Audit

Module 11: Performing ISO 27001 Audits

  • Preparing an Audit Report
  • Assessment of Audit Reports and Documents
  • Report Preparation, Findings, Reconciliation, and Conclusions
  • Auditing Procedures
  • Reviewing Documents and Reports
  • Classifying Findings
  • Reliability of Audit Findings

Module 12: Internal Auditor

  • Roles and Responsibilities
  • Audit Plan
  • Opening Meeting
  • Record Review Activities
  • Internal Auditor Checklist
  • Communication Between Departments
  • Drafting Reports and Test Plans

Module 13: ISMS and the ISO 27001 Standards Family

  • What is an ISMS?
  • Project Plan
  • Management and Governance Frameworks
  • ISMS Benefits
  • Scope of ISMS in an organisation
  • Introduction to Management Systems
  • Process Approach
  • Fundamentals
  • PDCA Cycle

Module 14: Interaction with ISO 27005

  • What is ISO 27005?
  • ISO 27001 VS ISO 27005
  • Quantifying the Business Impact
  • Impact Severity

Module 15: Roles and Responsibilities of a Lead Implementer

  • Roles and Responsibilities
  • Case Study: ABC’s ISO 27001

Module 16: Launch and Implement an ISMS in an Organisation

  • Apply the Frameworks
  • Procedures and Controls
  • Implementing the Controls
  • Training and Awareness Programme
  • Management’s Role
  • Responsibilities of Employees

Module 17: Risk Management

  • Analysing and Evaluating Risks
  • Managing Risk Approaches
  • Case Study: Law Firm

Module 18: Risk Assessment and the Statement of Applicability (SOA)

  • Risk Assessment
  • Conducting Risk Assessments
  • Risk Assessment Methodology
  • ISMS Risk Assessment Report
  • Threats and Vulnerabilities

Module 19: Introduction to ISO 27001 Lead Auditor

  • Roles and Responsibilities of a Lead Auditor
  • Team Selection and Planning
  • Qualifications of an Auditor
  • Conformance and Compliance

Module 20: Preparing and Planning an Audit

  • Roles and Responsibility of an Auditor
  • Auditing Schedule and Time
  • Procedures and Process Flow
  • Activities of an Auditor
  • Audit Components
  • Purpose and Extent of an Audit

Module 21: Reviewing Process and Qualities

  • Different Review Stages
  • Collecting Evidence
  • Observation
  • Audit Findings
  • Conducting Follow-ups

Module 22: Certification

  • Selecting an ISO 27001 Registrar
  • Prepare for the Certification Audits
  • Certification
  • Stage 1 Audit
  • Stage 2 Audit
  • Surveillance Audit
  • Re-Certification Audit

Module 23: Audit Triangle

  • Fraud Triangle
  • Tackling the Fraud Triangle

Module 24: Auditing Techniques

  • Classifying Audit Findings
  • On-Site Auditing
  • Remote Auditing Methods

Module 25: Tasks of an Auditor

  • Opening Meetings
  • Daily Discussion Meetings
  • Closing Meeting
  • Monitoring and Logging
  • Handling Stressful Situations
  • Intrusion and Penetration Testing
  • Reporting Audits
  • Follow-up Actions

Show moredown

Who Should Attend this ISO 27001 Lead Auditor Course?

Our ISO 27001 Lead Auditor Course is designed for professionals responsible for auditing, evaluating, and overseeing Information Security Management Systems (ISMS). The following professionals can benefit from this course:

  • Information Security Managers
  • Compliance Officers
  • Auditors
  • Risk Managers
  • Cybersecurity Engineers
  • Compliance Officers
  • Data Protection Officers

Prerequisites for the ISO 27001 Lead Auditor Course 

There are no formal prerequisites to attend this ISO 27001 Lead Auditor Course. However, familiarity with information security and ISO 27001 standards can be beneficial for the delegates.

ISO 27001 Lead Auditor Course Overview

ISO 27001 Lead Auditor Training provides in-depth knowledge of auditing Information Security Management Systems in line with ISO/IEC 27001 standards. Delegates learn auditing principles, risk assessment approaches, ISMS requirements, and techniques for evaluating conformity and audit evidence.

Delegates develop the ability to plan, conduct, and manage ISMS audits confidently. They strengthen their skills in collecting evidence, evaluating findings, preparing audit reports, communicating conclusions, and supporting effective audit follow-up activities.

This 5-Day course offered by The Knowledge Academy equips delegates to apply structured auditing techniques in professional environments. They will be better prepared to conduct ISO 27001 audits, classify findings, report audit results, and contribute to the continual improvement of an organisation’s ISMS.

ISO 27001 Lead Auditor Course Objectives

  • To understand the principles and requirements of ISO/IEC 27001 and ISMS auditing
  • To plan and conduct ISMS audits using structured auditing approaches
  • To evaluate audit evidence and assess conformity with ISO 27001 requirements
  • To identify, classify, and communicate audit findings effectively
  • To understand Information Security risk assessment and risk treatment approaches
  • To develop skills in reporting audit results and supporting follow-up activities

Learning Outcome of this ISO 27001 Lead Auditor Course

Upon completing this ISO 27001 Lead Auditor Course, delegates will be able to plan, conduct, report, and follow up on ISO 27001 audits. They will also be able to evaluate audit evidence, classify findings, assess ISMS performance, and identify opportunities for corrective action and continual improvement.

Career Benefits of this ISO 27001 Lead Auditor Course

Our ISO 27001 Lead Auditor Course develops specialised knowledge of ISMS auditing principles, audit procedures, and ISO/IEC 27001 requirements. These capabilities support professional development in information security auditing and compliance. The following are some of the key career benefits:

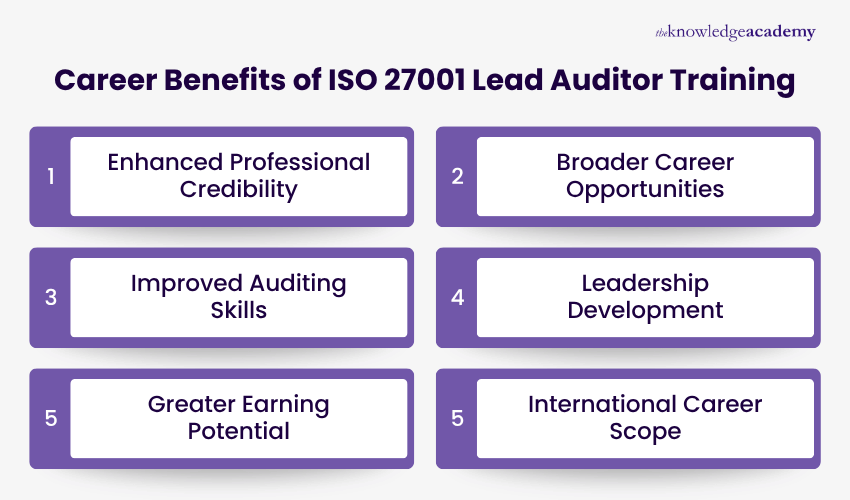
Career benefits of ISO 27001 Lead Auditor Training, including auditing skills, leadership, credibility and career opportunities

  • Enhanced Professional Credibility: Build recognised expertise in ISO 27001 requirements, ISMS auditing, and information security practices.
  • Broader Career Opportunities: Develop skills relevant to roles such as Lead Auditor, Information Security Consultant, Compliance Manager, and Risk Management Specialist.
  • Improved Auditing Skills: Strengthen your ability to plan audits, collect evidence, identify nonconformities, prepare reports, and support follow-up actions.
  • Leadership Development: Build confidence in leading audit activities, coordinating audit teams, and supporting organisations through certification and compliance requirements.
  • Greater Earning Potential: Advanced ISO 27001 auditing skills can strengthen your professional profile and support progression into higher-responsibility information security and compliance roles.
  • International Career Scope: ISO 27001 is globally recognised, helping professionals apply their auditing and information security knowledge across different industries and international environments.

Show moredown

What’s Included in this ISO 27001 Lead Auditor Course?

  • ISO 27001 Lead Auditor Examination
  • World-Class Training Sessions from Experienced Instructors
  • ISO 27001 Lead Auditor Certificate
  • Digital Delegate Pack

Show moredown

ISO 27001 Lead Auditor Exam Information

To achieve the ISO 27001 Lead Auditor Certification, candidates will need to sit for an examination. The exam format is as follows: 

  • Question Type: Multiple Choice 
  • Total Questions: 30 
  • Total Marks: 30 Marks 
  • Pass Mark: 50%, or 15/30 Marks 
  • Duration: 40 Minutes  
  • Open Book/ Closed Book: Closed Book

Show moredown

Online Instructor-led (2 days)

Online Self-paced (16 hours)

ISO 27001 Internal Auditor Exam

ISO 27001 Internal Auditor Course Outline

Module 1: Introduction to ISO 27001

  • Introduction
  • Compatibility with Other Management System Standards
  • ISO 27001:2022 and Its Clauses

Module 2: Information Security

  • What is Business?
  • Industries
  • Risk
  • SWOT Analysis
  • Constructs and Characteristics of Assets
  • Security and Privacy
  • Triad of Information Security
  • Cyber Security is Everyone’s Responsibility
  • Cybersecurity Landscape
  • What is Information Security?
  • Information Security Management
  • Need of Information Security
  • Threats to Information Security
  • Active and Passive Attacks

Module 3: Context of the Organisation

  • Understanding the Organisation and Its Context
  • Understanding the Needs and Expectations of Interested Parties
  • Determining the Scope of the Information Security Management System
  • Information Security Management System

Module 4: Leadership

  • Leadership and Commitment
  • Policy
  • Organisational Roles, Responsibilities, and Authorities

Module 5: Planning

  • Organisational Roles, Responsibilities, and Authorities
  • Information Security Objectives and Planning to Achieve Them
  • Planning of Changes

Module 6: Support

  • Resources
  • Competence
  • Awareness
  • Communication
  • Documented Information

Module 7: Operation

  • Operational Planning and Control
  • Information Security Risk Assessment
  • Information Security Risk Treatment

Module 8: Performance Evaluation

  • Monitoring, Measurement, Analysis, and Evaluation
  • Internal Audit
  • Management Review

Module 9: Improvement

  • Nonconformity and Corrective Action
  • Continual Improvement

Module 10: Introduction to Auditing

  • Internal Audit Charter
  • Communicate with Organisation and Audit Committee
  • Auditing Reflects
  • General and Internal Auditing Standards and Guidance
  • Auditing Types
  • Auditing Techniques
  • Auditing Principles
  • Phases of Audit

Module 11: Performing ISO 27001 Audits

  • Preparing an Audit Report
  • Assessment of Audit Reports and Documents
  • Report Preparation, Findings, Reconciliation, and Conclusions
  • Auditing Procedures
  • Reviewing Documents and Reports
  • Classifying Findings
  • Reliability of Audit Findings

Module 12: Internal Auditor

  • Roles and Responsibilities
  • Audit Plan
  • Opening Meeting
  • Record Review Activities
  • Internal Auditor Checklist
  • Communication Between Departments
  • Drafting Reports and Test Plans

Show moredown

Who Should Attend this ISO 27001 Internal Auditor Training Course?

Our ISO 27001 Internal Auditor Course is designed for professionals responsible for assessing internal information security practices and supporting compliance with ISO/IEC 27001 requirements. The following professionals can benefit from this course:

  • Internal Auditors
  • Information Security Managers
  • IT Managers
  • Cybersecurity Engineers
  • Risk Managers
  • Compliance Officers
  • ISMS Managers
  • Governance Professionals

Prerequisites for the ISO 27001 Internal Auditor Training Course

There are no formal prerequisites to attend this ISO 27001 Internal Auditor Course. However, familiarity with Information Security principles and concepts can be beneficial for the delegates.

ISO 27001 Internal Auditor Training Course Overview

ISO 27001 Internal Auditor Course develops the skills required to conduct internal audits of an Information Security Management System against ISO/IEC 27001 requirements. It covers audit principles, evidence evaluation, nonconformities, reporting, and continual improvement.

Delegates will develop practical knowledge of audit planning, evidence review, audit techniques, findings, and reporting. They will also understand how internal audits support ISMS performance, corrective action, and continual improvement.

This 2-Day course by The Knowledge Academy helps delegates apply ISO 27001 internal auditing practices in organisational environments. Delegates will be better prepared to conduct structured audits, communicate findings, and support effective ISMS improvement.

ISO 27001 Internal Auditor Training Course Objectives

  • To understand ISO/IEC 27001 requirements and the structure of an ISMS
  • To understand internal audit principles, standards, techniques, and responsibilities
  • To plan and prepare ISO 27001 internal audits effectively
  • To review audit evidence, documents, records, and organisational processes
  • To classify audit findings and prepare clear internal audit reports
  • To support nonconformity resolution, corrective action, and continual improvement

Learning Outcome of this ISO 27001 Internal Auditor Course

Upon completing this ISO 27001 Internal Auditor Training, delegates will be able to plan, conduct, and report internal audits of an ISMS against ISO 27001 requirements. They will also be able to evaluate audit evidence, identify nonconformities, support corrective actions, and contribute to continual improvement.

Benefits of this ISO 27001 Internal Auditor Course

Our ISO 27001 Internal Auditor Course provides structured learning in the principles and practices of internal auditing within an Information Security Management System (ISMS). It helps delegates understand the importance of systematic audits in maintaining information security standards. The following are some of the key benefits of this course:

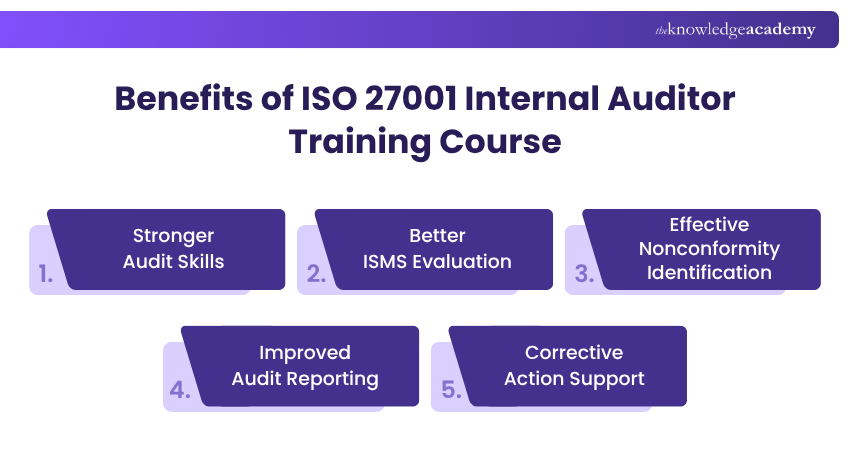
Benefits of ISO 27001 Internal Auditor Training Course

  • Stronger Audit Skills: Develop practical knowledge of audit principles, techniques, planning, execution, and reporting.
  • Better ISMS Evaluation: Understand how to review ISMS processes, documented information, risk activities, and organisational practices.
  • Effective Nonconformity Identification: Learn to identify, classify, and document audit findings accurately.
  • Improved Audit Reporting: Build skills for preparing clear audit reports, conclusions, and supporting documentation.
  • Corrective Action Support: Understand how audit findings contribute to corrective action and continual improvement.

Career Opportunities After Completing this ISO 27001 Internal Auditor Course

Completing this training can support professionals seeking roles involving information security auditing, compliance, risk, and ISMS assurance. Potential career opportunities include:

  • ISO 27001 Internal Auditor: Conduct internal ISMS audits, review evidence, identify findings, and prepare audit reports.
  • Information Security Auditor: Evaluate information security processes and assess their alignment with organisational and ISO/IEC 27001 requirements.
  • Compliance Analyst: Support compliance activities by reviewing processes, documentation, risks, and corrective actions.
  • Risk and Assurance Analyst: Assist with risk assessment, assurance activities, audit evidence, and organisational controls.
  • ISMS Manager: Support the operation, evaluation, and continual improvement of an Information Security Management System.

Show moredown

What’s Included in this ISO 27001 Internal Auditor Training Course?

  • ISO 27001 Internal Auditor Examination
  • World-class Training Sessions from Experienced Instructors
  • Interactive Learning with 24*7 Support
  • Digital Delegate Pack

Show moredown

ISO 27001 Internal Auditor Exam Information 

To achieve the ISO 27001 Internal Auditor, candidates will need to sit for an examination. The exam format is as follows: 

  • Question Type: Multiple Choice 
  • Total Questions: 30 
  • Total Marks: 30 Marks 
  • Pass Mark: 50%, or 15/30 Marks 
  • Duration: 40 Minutes
  • Open Book/ Closed Book: Closed Book

Show moredown

Online Instructor-led (3 days)

Online Self-paced (24 hours)

ISO 27001 Lead Implementer Exam

ISO 27001 Lead Implementer Course Outline

Module 1: Introduction to ISO 27001

  • Introduction
  • Compatibility with Other Management System Standards
  • ISO 27001:2022 and Its Clauses

Module 2: Information Security

  • What is Business?
  • Industries
  • Risk
  • SWOT Analysis
  • Constructs and Characteristics of Assets
  • Security and Privacy
  • Triad of Information Security
  • Cyber Security is Everyone’s Responsibility
  • Cybersecurity Landscape
  • What is Information Security?
  • Information Security Management
  • Need of Information Security
  • Threats to Information Security
  • Active and Passive Attacks

Module 3: Context of the Organisation

  • Understanding the Organisation and Its Context
  • Understanding the Needs and Expectations of Interested Parties
  • Determining the Scope of the Information Security Management System
  • Information Security Management System

Module 4: Leadership

  • Leadership and Commitment
  • Policy
  • Organisational Roles, Responsibilities, and Authorities

Module 5: Planning

  • Organisational Roles, Responsibilities, and Authorities
  • Information Security Objectives and Planning to Achieve Them
  • Planning of Changes

Module 6: Support

  • Resources
  • Competence
  • Awareness
  • Communication
  • Documented Information

Module 7: Operation

  • Operational Planning and Control
  • Information Security Risk Assessment
  • Information Security Risk Treatment

Module 8: Performance Evaluation

  • Monitoring, Measurement, Analysis, and Evaluation
  • Internal Audit
  • Management Review

Module 9: Improvement

  • Nonconformity and Corrective Action
  • Continual Improvement

Module 10: Introduction to Auditing

  • Internal Audit Charter
  • Communicate with Organisation and Audit Committee
  • Auditing Reflects
  • General and Internal Auditing Standards and Guidance
  • Auditing Types
  • Auditing Techniques
  • Auditing Principles
  • Phases of Audit

Module 11: Performing ISO 27001 Audits

  • Preparing an Audit Report
  • Assessment of Audit Reports and Documents
  • Report Preparation, Findings, Reconciliation, and Conclusions
  • Auditing Procedures
  • Reviewing Documents and Reports
  • Classifying Findings
  • Reliability of Audit Findings

Module 12: Internal Auditor

  • Roles and Responsibilities
  • Audit Plan
  • Opening Meeting
  • Record Review Activities
  • Internal Auditor Checklist
  • Communication Between Departments
  • Drafting Reports and Test Plans

Module 13: ISMS and the ISO 27001 Standards Family

  • What is an ISMS?
  • Project Plan
  • Management and Governance Frameworks
  • ISMS Benefits
  • Scope of ISMS in an Organisation
  • Introduction to Management Systems
  • Process Approach
  • Fundamentals
  • PDCA Cycle

Module 14: Interaction with ISO 27005

  • What is ISO 27005?
  • ISO 27001 VS ISO 27005
  • Quantifying the Business Impact
  • Impact Severity

Module 15: Roles and Responsibilities of a Lead Implementer

  • Roles and Responsibilities
  • Case Study:  ABC’s ISO 27001 

Module 16: Launch and Implement an ISMS in an Organisation

  • Apply the Frameworks
  • Procedures and Controls
  • Implementing the Controls
  • Training and Awareness Programme
  • Management’s Role
  • Responsibilities of Employees

Show moredown

Who Should Attend this ISO 27001 Lead Implementer Training?

This ISO 27001 Lead Implementer Course is suitable for professionals involved in establishing, implementing, managing, or improving Information Security Management Systems in line with ISO 27001 requirements. The following professionals can benefit from attending this course:

  • Security Consultants
  • Compliance Officers
  • Information Security Managers
  • Risk Managers
  • Cybersecurity Engineers
  • Auditors
  • Compliance Managers

Prerequisites for the ISO 27001 Lead Implementer Training

There are no formal prerequisites to attend this ISO 27001 Lead Implementer Course. However, familiarity with ISO 27001 standard and information security principles will be beneficial for the delegates.

ISO 27001 Lead Implementer Training Overview

ISO 27001 Lead Implementer Training provides delegates with the skills required to manage an Information Security Management System (ISMS) in accordance with ISO 27001. It focuses on risk management, control implementation, and continual improvement practices.

This training enhances delegates’ ability to lead ISMS implementation projects and strengthen organisational information security frameworks. It builds structured competence in managing documentation, audits, and risk treatment processes.

This 3-Day course offered by The Knowledge Academy enables delegates to apply ISO 27001 principles confidently within real-world environments. Delegates will be able to coordinate implementation activities, support employee awareness, monitor ISMS performance, and address nonconformities.

ISO 27001 Lead Implementer Training Course Objectives

  • To understand ISO 27001 principles, requirements, and terminology
  • To perform risk assessments and define appropriate risk treatment plans
  • To establish, implement, and manage an effective ISMS
  • To document and maintain compliance with ISO 27001 standards
  • To implement Information Security procedures and controls within an organisation
  • To apply continual improvement processes within the ISMS framework

Learning Outcome of this ISO 27001 Lead Implementer Training

Upon completing this course, delegates will be equipped to establish, implement, manage, and improve an ISMS within an organisation. They will also develop the confidence to manage risk treatment, apply controls, support internal audits, and lead ISO 27001 implementation activities within an organisation.

Key Benefits of this ISO 27001 Lead Implementer Certification

This ISO 27001 Lead Implementer Certification helps professionals strengthen their ability to establish, manage, and improve Information Security Management Systems in line with ISO 27001 requirements. Key benefits include:

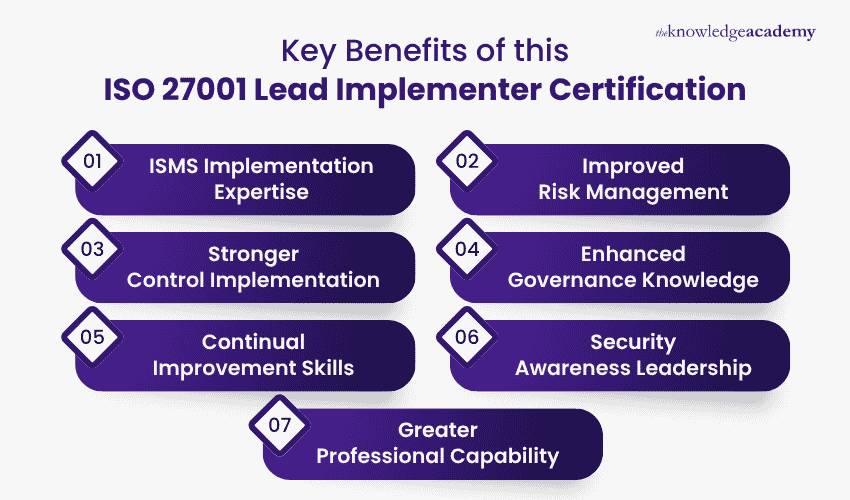
7 benefits of ISO 27001 Lead Implementer Certification—ISMS skills, risk management, governance, and more

  • ISMS Implementation Expertise: Develop the knowledge required to establish, implement, manage, and improve an Information Security Management System.
  • Improved Risk Management: Build skills in conducting risk assessments, evaluating risks, and applying appropriate risk treatment approaches.
  • Stronger Control Implementation: Learn how to apply frameworks, procedures, and controls that support organisational information security objectives.
  • Enhanced Governance Knowledge: Understand leadership responsibilities, organisational roles, policies, and governance requirements within an ISMS.
  • Continual Improvement Skills: Develop the ability to support corrective actions, performance evaluation, management reviews, and continual ISMS improvement.
  • Security Awareness Leadership: Gain knowledge of training and awareness programmes that help employees understand their information security responsibilities.
  • Greater Professional Capability: Strengthen practical expertise in ISO 27001 implementation, risk management, governance, and ISMS management to support broader information security responsibilities.

Career Opportunities After Completing this ISO 27001 Lead Implementer Training

Completing this ISO 27001 Lead Implementer Course can support career progression across information security, ISMS implementation, risk management, governance, and compliance roles. Potential career opportunities include:

  • Information Security Manager: Oversee information security practices, ISMS implementation, risk treatment, and continual improvement activities.
  • ISMS Manager: Manage the establishment, operation, monitoring, and improvement of an organisation’s Information Security Management System.
  • Information Security Consultant: Support organisations in implementing ISO 27001 requirements, defining ISMS scope, applying controls, and improving security practices.
  • Risk Manager: Assess information security risks, evaluate their potential impact, and support appropriate risk treatment approaches.
  • Compliance Manager: Support compliance with ISO 27001 requirements by managing policies, documented information, controls, and governance activities.
  • Internal Auditor: Review ISMS processes, evaluate conformity, assess documented information, and support corrective actions and continual improvement.

Show moredown

What’s Included in this ISO 27001 Lead Implementer Training Course?

  • ISO 27001 Lead Implementer Examination
  • World-Class Training Sessions from Experienced Instructors
  • ISO 27001 Lead Implementer Certificate
  • Digital Delegate Pack

Show moredown

ISO 27001 Lead Implementer Exam Information

To achieve the ISO 27001 Lead Implementer, candidates will need to sit for an examination. The exam format is as follows: 

  • Question Type: Multiple Choice 
  • Total Questions: 30 
  • Total Marks: 30 Marks 
  • Pass Mark: 50%, or 15/30 Marks 
  • Duration: 40 Minutes  
  • Open Book/ Closed Book: Closed Book

Show moredown

Not sure which course to choose?

Speak to a training expert for advice if you are unsure of what course is right for you. Give us a call on +48 221041849 or Enquire.

Skills You Will Gain from Our ISO 27001 Training

ISO 27001 Training by The Knowledge Academy provides learners with an understanding of Information Security Management, focusing on implementing, maintaining, and auditing systems aligned with international standards. Here are the skills you will gain after training:

  • Information Security Management: Gain expertise in creating and overseeing an ISO 27001-compliant ISMS framework for data protection and governance.
  • Risk Assessment & Treatment: Professionals get skilled in finding and reducing information security threats.
  • Compliance & Audit Preparation: Develop proficiency in preparing for ISO 27001 audits and making sure that the information security regulations are followed.
  • Security Controls Implementation: Learners gain knowledge in security controls to effectively safeguard private data, networks, and assets.
  • Continuous Improvement: Learn to monitor, evaluate, and improve ISMS performance using the PDCA (Plan-Do-Check-Act) cycle.
     

Career Opportunities After ISO 27001 Courses

Career Opportunities After ISO 27001 Courses

Obtaining an ISO 27001 Certification opens doors to various opportunities in multiple industries. Below are some of the roles you can pursue after certification:

  • Information Security Manager: Maintain ISO 27001 accreditation by overseeing ISMS implementation and continual improvement.
  • ISO 27001 Lead Auditor: Conduct independent ISMS audits to verify compliance and recommend enhancements.
  • Compliance Officer: Ensure organisational adherence to ISO standards, minimising risks and regulatory penalties.
  • Risk Manager: Identify vulnerabilities and implement mitigation strategies to manage potential threats effectively.
  • IT Security Consultant: Advise organisations on data protection, system integrity, and achieving ISO certifications.
  • Cybersecurity Analyst: Monitor systems and implement preventive controls in line with ISO 27001 requirements.
  • Data Protection Specialist: Manage privacy policies and ensure compliance with global data protection regulations.
  • Internal Auditor: Support continuous ISMS improvement and verify ongoing compliance with ISO 27001 standards.
     

How to Choose the Right ISO 27001 Training

Choosing the right ISO 27001 Training Course depends on your existing knowledge, career goals, and professional responsibilities. The Knowledge Academy offers a range of courses designed to help delegates develop essential skills in information security management, auditing, and ISMS implementation.

  • ISO 27001 Foundation: Ideal for beginners seeking to understand ISO 27001 principles and ISMS requirements.
  • ISO 27001 Internal Auditor: Suitable for professionals responsible for conducting internal audits and evaluating ISMS effectiveness.
  • ISO 27001 Lead Auditor: Designed for professionals aiming to plan, manage, and lead ISO 27001 audits.
  • ISO 27001 Lead Implementer: Ideal for individuals responsible for establishing, implementing, and improving an ISMS within their organisation.
Show more blue-arrow

Package deals for ISO 27001 Training

Our training experts have compiled a range of course packages on a variety of categories in ISO 27001 Training, to boost your career. The packages consist of the best possible qualifications with ISO 27001 Training, and allows you to purchase multiple courses at a discounted rate.

Swipe for more. Don’t miss out!

ISO 27001 Training FAQs

ISO 27001 is an international standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). It helps organisations manage information security risks and protect the confidentiality, integrity, and availability of information.

The ISO 27001 Foundation Course provides a basic understanding of ISO 27001 and Information Security Management System (ISMS) requirements. The Internal Auditor Course focuses on conducting internal ISMS audits, while the Lead Auditor Course develops the skills to plan, manage, and lead ISMS audits. The Lead Implementer Course focuses on establishing, implementing, managing, and continually improving an ISMS.

Our ISO 27001 Training covers information security management principles, Information Security Management System (ISMS) requirements, risk assessment, and risk treatment. Depending on the course selected, delegates explore internal and lead auditing procedures, ISMS implementation, compliance requirements, and continual improvement practices.

The Knowledge Academy's ISO 27001 Training includes world-class training sessions from experienced instructors, a Digital Delegate Pack containing essential course materials, and access to the MyTKA Training Portal. Delegates will also undertake the relevant examination based on their selected course.

Yes, our ISO 27001 Training Courses cover the latest ISO/IEC 27001:2022 standard, including ISMS requirements, risk management principles, and Annex A information security controls. These courses equip delegates with the knowledge and skills to strengthen information security, manage risks, and support ISO 27001 compliance within their organisations.

There are no formal prerequisites for attending these ISO 27001 Certification Courses. However, a basic understanding of information security concepts and ISO 27001 standards can be beneficial for delegates. 

As a trusted training provider, The Knowledge Academy offers ISO 27001 Training Courses with durations that vary depending on the course selected. Delegates can visit the relevant course page to check the exact duration, available delivery formats, and training details.

Yes, we offer ISO 27001 Online Courses through flexible learning options, including Online Instructor-Led and Self-Paced Training, depending on the course selected. Delegates can visit the relevant course page to explore available delivery formats and choose an option that suits their schedule and professional commitments.

Yes, as a global training provider, we offer self-paced options for ISO 27001 Training, allowing delegates to study at their own pace and convenience. This flexible learning approach helps professionals develop their information security management skills while balancing personal and professional commitments.

Yes, our ISO 27001 Training Courses cover different areas of information security management, auditing, and ISMS implementation, allowing delegates to build their knowledge progressively. Delegates can contact our dedicated customer support team for guidance on selecting and combining suitable courses to create a structured learning path aligned with their professional goals.

Yes, The Knowledge Academy's ISO 27001 Courses help organisations prepare for certification audits by developing essential skills in ISMS implementation, risk management, and auditing. These courses equip delegates with the knowledge to assess information security controls, identify areas for improvement, and support compliance with ISO 27001 standards.

Yes, The Knowledge Academy's ISO 27001 Training Courses include an examination to assess delegates' understanding of key concepts and principles. These examinations help evaluate their knowledge and skills in information security management and ISO 27001 standards.

For individuals, ISO 27001 Training develops skills in information security, risk management, auditing, compliance, and ISMS implementation. For organisations, these capabilities can strengthen internal security practices, improve risk management, support ISMS maintenance, and help teams prepare for certification and continual improvement activities.

The Knowledge Academy provides dedicated learning support throughout ISO 27001 Training. Delegates benefit from interactive learning sessions and 24/7 support to address course-related queries, overcome learning challenges, and ensure a smooth training experience.

Yes, The Knowledge Academy offers post-training support to assist delegates with course-related queries and other enquiries. Our dedicated customer support team is available to provide guidance and assistance whenever delegates need further information after completing their training.

Yes, The Knowledge Academy provides corporate and onsite ISO 27001 Training for organisations and teams. Training can support workforce development in areas such as ISMS implementation, internal auditing, risk management, compliance, and information security responsibilities.

As a trusted training provider, The Knowledge Academy offers a range of ISO 27001 Courses covering Foundation, Internal Auditor, Lead Auditor, and Lead Implementer levels. Delegates can benefit from experienced instructors, flexible learning formats, structured course resources, and dedicated learning support.

The Knowledge Academy is one of the Leading global training provider for ISO 27001 Training.

The training fees for ISO 27001 Training in Poland starts from €2895

Show more down

Why we're the go to training provider for you
icon

Best price in the industry

You won't find better value in the marketplace. If you do find a lower price, we will beat it.
icon

Trusted & Approved

Recognised by leading certification bodies, we deliver training you can trust.
icon

Many delivery methods

Flexible delivery methods are available depending on your learning style.
icon

High quality resources

Resources are included for a comprehensive learning experience.
barclays Logo
deloitte Logo
Thames Water Logo

"Really good course and well organised. Trainer was great with a sense of humour - his experience allowed a free flowing course, structured to help you gain as much information & relevant experience whilst helping prepare you for the exam"

Joshua Davies, Thames Water

santander logo
bmw Logo
Google Logo
cross

Exclusive Deals For Future Leaders!

friday-sale UP TO 60% OFF!

* WHO WILL BE FUNDING THE COURSE?

close

close

Thank you for your enquiry!

One of our training experts will be in touch shortly to go over your training requirements.

close

close

Press esc to close

close close

Back to course information

Thank you for your enquiry!

One of our training experts will be in touch shortly to go overy your training requirements.

close close

Thank you for your enquiry!

One of our training experts will be in touch shortly to go over your training requirements.