CISSP Courses

Online Instructor-led (5 days)

Online Self-paced (40 hours)

CISSP Training Course Outline

Domain 1: Security and Risk Management

  • Understand, Adhere to, and Promote Professional Ethics
    • Code of Professional Ethics
    • Organisational Code of Ethics
  • Understand and Apply Security Concepts
    • Overview
    • Confidentiality
    • Integrity
    • Availability
    • Authenticity
    • Nonrepudiation
  • Evaluate and Apply Security Governance Principles
    • Security Governance
    • Alignment of Security Function to Business Strategy, Goals, Mission, and Objectives
    • Organisational Processes
    • Organisational Roles and Responsibilities
    • Security Control Frameworks
    • Due Care and Due Diligence
  • Legal and Regulatory Issues that Pertain to Information Security in a Global Context
    • Cybercrimes and Data Breaches
    • Licensing and Intellectual Property Requirements
    • Import/Export Controls
    • Transborder Data Flow
    • Issues Related to Privacy
    • Contractual, Legal, Industry Standards, and Regulatory Requirements
  • Requirements for Investigation Types (i.e., Administrative, Criminal, Civil, Regulatory, Industry Standards) 
    • Understand Requirements for Investigation Types
  • Develop, Document, and Implement Security Policy, Standards, Procedures, and Guidelines 
    • Introduction
    • Security Policies
    • Security Policies and Individuals
    • Acceptable Use Policy
    • Security Standards, Baselines, and Guidelines
  • Identify, Analyse, and Prioritise Business Continuity (BC) Requirements
    • Introduction
    • Business Impact Analysis
    • External Dependencies
  • Contribute to and Enforce Personnel Security Policies and Procedures 
    • Candidate Screening and Hiring
    • Employment Agreements and Policy Driven Requirements
    • Onboarding, Transfers, and Termination Processes
    • Vendor, Consultant, and Contractor Agreements and Controls
  • Understand and Apply Risk Management Concepts 
    • Threat and Vulnerability Identification
    • Risk Analysis, Assessment, and Scope
    • Risk Response and Treatment
    • Applicable Types of Controls
    • Control Assessments
    • Continuous Monitoring and Measurement
    • Reporting
    • Continuous improvement 
    • Risk frameworks
  • Understand and Apply Threat Modeling Concepts and Methodologies
    • Introduction
    • Identifying Threats
    • Determining and Diagramming Potential Attacks
    • Performing Reduction Analysis
    • Prioritisation and Response
  • Apply Supply Chain Risk Management (SCRM) Concepts
    • Risks Associated with the Acquisition of Products and Services from Suppliers and Providers
    • Risk Mitigations
  • Establish and Maintain a Security Awareness, Education, and Training Program
    • Methods and Techniques to Increase Awareness and Training
    • Periodic Content Reviews to Include Emerging Technologies and Trends 
    • Program Effectiveness Evaluation

Domain 2: Asset Security

  • Identify and Classify Information and Assets
    • Data Classification
    • Asset Classification
  • Establish Information and Asset Handling Requirements
    • Establish Information and Asset Handling Requirements
  • Provision Information and Assets Securely
    • Information and Asset Ownership
    • Asset Inventory
    • Asset Management
  • Manage Data Lifecycle (e.g., EOL and EOS)
    • Data Roles
    • Data Collection
    • Data Location
    • Data Maintenance
    • Data Retention
    • Data Remanence
    • Data Destruction
  • Ensure Appropriate Asset Retention 
    • Ensure Appropriate Asset Retention (e.g., EOL and EOS)
  • Determine Data Security Controls and Compliance Requirements
    • Data States
    • Scoping and Tailoring
    • Standards Selection
    • Data Protection Methods

Domain 3: Security Architecture and Engineering

  • Research, Implement and Manage Engineering Processes Using Secure Design Principles
    • Overview of Research, Implement and Manage Engineering Processes
  • Understand the Fundamental Concepts of Security Models
    • Fundamental Concepts of Security Models 
  • Select Controls Based Upon Systems Security Requirements
    • Overview of Select Controls Based Upon Systems Security Requirements
  • Understand Security Capabilities of Information Systems
    • Security Capabilities of Information Systems
  • Assess And Mitigate the Vulnerabilities of Security Architectures, Designs, and Solution Elements
    • Assess and Mitigate Security Vulnerabilities
  • Select and Determine Cryptographic Solutions
    • Cryptographic Lifecycle
    • Cryptographic Methods
    • Public Key Infrastructure
  • Understand Methods of Cryptanalytic Attacks
    • Methods of Cryptanalytic Attacks
  • Apply Security Principles to Site And Facility Design
    • Overview of Apply Security Principles to Site and Facility Design
  • Design Site And Facility Security Controls
    • Design Site and Facility Security Controls
    • Wiring Closets
    • Server Rooms/Data Centres
    • Media Storage Facilities
    • Evidence Storage
    • Restricted and Work Area Security
    • Utilities and HVAC
    • Environmental Issues
    • Fire prevention, detection, and suppression
    • Power
  • Manage the information system lifecycle
    • Stakeholders Needs and Requirements
    • Requirements Analysis
    • Architectural Design
    • Development/Implementation
    • Integration
    • Verification and Validation
    • Transition/Deployment
    • Operations and Maintenance/Sustainment
    • Retirement/Disposal

Domain 4: Communication and Network Security

  • Apply Secure Design Principles in Network Architectures
    • Open System Interconnection (OSI) and Transmission Control Protocol
    • Internet Protocol (IP) Version 4 and 6 (IPv6)
    • Secure Protocols 
    • Implications of Multilayer Protocols
    • Converged Protocols
    • Transport Architecture
    •  Performance Metrics
    • Traffic Flows
    • Physical Segmentation
    • Logical Segmentation
    • Micro-Segmentation
    • Edge Networks
    • Wireless Networks
    • Cellular/Mobile Networks 
    • Content Distribution Networks
    • Software Defined Networks (SDN)
    • Virtual Private Cloud (VPC)
    • Monitoring and Management
  • Secure Network Components
    • Operation of Infrastructure
    • Transmission Media
    • Network Access Control
    • Endpoint Security
  • Implement Secure Communication Channels According to Design 
    • Voice, Video, and Collaboration 
    • Remote Access
    • Data Communications
    • Third-party Connectivity

Domain 5: Identity and Access Management (IAM)

  • Control Physical and Logical Access to Assets
    • Information
    • Systems
    • Devices
    • Facilities
    • Applications
    • Services 
  • Design Identification and Authentication Strategy
    • Groups and Roles
    • Authentication, Authorisation and Accounting (AAA)
    • Session Management
    • Registration, Proofing, and Establishment of Identity
    •  Federated Identity Management (FIM)
    • Credential Management Systems
    • Single sign-on (SSO)
    • Just-In-Time
  • Integrate Identity as a Third-Party Service 
    • On-premises
    • Cloud
    • Hybrid 
  • Implement and Manage Authorisation Mechanisms
    • Role-Based Access Control (RBAC)
    • Rule based access control
    • Mandatory Access Control (MAC)
    • Discretionary Access Control (DAC)
    • Attribute-based Access Control (ABAC)
    •  Risk-based Access Control
    • Access Policy Enforcement
  • Manage the Identity and Access Provisioning Lifecycle 
    • Account Access Review
    • Provisioning and Deprovisioning
    • Role Definition and Transition
    • Privilege Escalation
    • Service Accounts Management
  • Implement Authentication Systems 
    • Overview of Implement Authentication Systems 

Domain 6: Security Assessment and Testing

  • Design and Validate Assessment, Test, and Audit Strategies 
    • Internal
    • External
    • Third-party
    • Location 
  • Conduct Security Control Testing 
    • Vulnerability Assessment
    • Penetration Testing
    • Log Reviews
    • Synthetic Transactions/Benchmarks
    • Code Review and Testing
    • Misuse Case Testing
    • Coverage Analysis
    • Interface Testing
    • Breach Attack Simulations
    • Compliance Checks 
  • Collect Security Process Data 
    • Account Management
    • Management Review and Approval
    • Key Performance and Risk Indicators
    • Backup Verification Data
    • Training and Awareness
    • Disaster Recovery (DR) and Business Continuity (BC)
  • Analyse Test Output and Generate Report 
    • Remediation
    • Exception Handling
    • Ethical Disclosure
  • Conduct or Facilitate Security Audits 
    • Internal
    • External
    • Third-party
    • Location

Domain 7: Security Operations

  • Understand and Comply with Investigations 
    • Evidence Collection and Handling  
    • Reporting and Documenting
    • Investigative Techniques
    • Digital Forensics Tools, Tactics, and Procedures
    • Artifacts (E.G., Data, Computer, Network, Mobile Device) 
  • Conduct Logging and Monitoring Activities 
    • Intrusion Detection and Prevention
    • Security Information and Event Management
    • Continuous Monitoring
    • Egress Monitoring
    • Log Management
    • Threat Intelligence (E.G., Threat Feeds, Threat Hunting)
    • User and Entity Behaviour Analytics (UEBA)
  • Perform Configuration Management
    • Apply Foundational Security Operations Concepts 
    • Applying Security Operations 
    • Need-to-know and Least Privilege 
    • Separation of Duties and Responsibilities 
    • Privileged Account Management 
    • Job Rotation
    • Service-Level Agreements 
  • Apply Resource Protection
    • Media Management
    • Media Protection Techniques
    • Data at Rest/Data in Transit
  • Conduct Incident Management
    • Detection
    • Response
    • Mitigation
    • Reporting
    • Recovery
    • Remediation
    • Lessons learned
  • Operate and Maintain Detective and Preventative Measures 
    • Sandboxing
    • Honeypots/Honeynets 
    • Anti-Malware 
    • Machine Learning and Artificial Intelligence (AI) Based Tools
  • Implement and Support Patch and Vulnerability Management
  • Participate in Change Management Processes
    • Change Management 
  • Implement Recovery Strategies
    • Backup Storage Strategies
    • Recovery Site Strategies
    • Multiple Processing Sites
    • System Resilience, High Availability (HA), Quality of Service (Qos), and Fault Tolerance
  • Implement Disaster Recovery Processes
    • Response
    • Personnel
    • Communications
    • Assessment
    • Restoration
    • Training and Awareness
    • Lessons learned
  • Test Disaster Recovery Plans
  • Participate in Business Continuity (BC) Planning and Exercises 
  • Implement and Manage Physical Security
  • Address Personnel Safety and Security Concerns 
    • Travel
    • Security Training and Awareness 
    • Emergency Management
    • Duress

Domain 8: Software Development Security

  • Understand and Integrate Security in the Software Development Life Cycle (SDLC)
    • Development Methodologies
    • Maturity Models 
    • Operation and Maintenance
    • Change Management
    • Integrated Product Team
  • Identify and Apply Security Controls in Software Development Ecosystems
    • Programming Languages
    • Libraries
    • Tool Sets
    • Integrated Development Environment
    • Runtime
    • Continuous Integration and Continuous Delivery (CI/CD)
    • Software Configuration Management (CM)
    • Code Repositories
    • Application Security Testing
  • Assess the Effectiveness of Software Security
    • Auditing and Logging of Changes
    • Risk Analysis and Mitigation
  • Assess Security Impact of Acquired Software 
    • Commercial-off-the-shelf (COTS)
    • Open Source
    • Third-party
    • Managed Services
    • Cloud Services
  • Define and Apply Secure Coding Guidelines and Standards
    • Security Weaknesses and Vulnerabilities at the Source-code Level 
    • Security of Application Programming Interfaces (API)
    • Secure Coding Practices
    • Software-defined Security
       

Show moredown

Who Should Attend this CISSP Training?

This CISSP Training is suitable for experienced IT and cyber security professionals who want to strengthen their knowledge across information security, governance, risk, architecture, and security operations. The following professionals can benefit from this training:

  • Information Security Professionals
  • Security Consultants
  • Security Managers
  • Security Analysts
  • Risk Management Specialists
  • Network Architects
  • Compliance Officers

Prerequisites for the CISSP Training

There are no formal prerequisites to attend this CISSP Training. However, prior knowledge of information security, networking, governance, risk management, or security operations will help delegates engage effectively with the course content.

CISSP Training Overview

CISSP Training introduces delegates to the principles and practices used to manage and protect information across complex organisational environments. It covers security and risk management, architecture, network security, IAM, operations, and software development security.

Delegates develop skills in assessing risks, evaluating controls, managing access, interpreting security requirements, and supporting secure operations. They also strengthen their understanding of architecture, testing, incident response, and security governance.

This 5-Day course helps delegates build structured information security knowledge across technical and management domains. They will be better equipped to support security decisions, risk management, and organisational security objectives.

CISSP Training Course Objectives

  • To understand key CISSP domains, including security and risk management and asset security
  • To explore security architecture, IAM, assessment, and testing principles
  • To understand legal, ethical, regulatory, and governance requirements
  • To develop knowledge of security policies, standards, procedures, and guidelines
  • To understand cryptographic principles and methods for protecting information
  • To explore secure architecture, engineering, and design approaches

Learning Outcomes of CISSP Training Course

Upon completing this CISSP Training, delegates will understand how security governance, risk management, architecture, access control, and operational security work together. They will be better equipped to interpret security requirements and support informed information security decisions.

Show moredown

What’s Included in this CISSP Training Course?

  • World-Class Training Sessions from Experienced Instructors
  • Interactive Learning with 24*7 Support
  • Digital Delegate Pack

Show moredown

Online Instructor-led (4 days)

Online Self-paced (32 hours)

CISSP-ISSAP Training Course Outline

Domain 1: Governance, Risk, and Compliance (GRC)

Module 1: Identify Legal, Regulatory, Organisational, and Industry Requirements
  • Applicable Information Security Standards and Guidelines
  • Third-Party and Contractual Obligations
  • Applicable Sensitive and Personal Data Standards and Privacy Regulations
  • Resilient Solutions
Module 2: Architecting for Governance, Risk, and Compliance
  • Identify Key Assets, Business Objectives, and Stakeholders
  • Design Monitoring and Reporting
  • Design for Auditability
  • Incorporate Risk Assessment Artifacts
  • Advise Risk Treatment

Domain 2: Security Architecture Modelling

Module 1: Identify Security Architecture Approach
  • Scope and Types of Security Architecture
  • Frameworks and Reference Architectures
  • Threat Modelling Frameworks
  • Common Vulnerability Scoring Systems
Module 2: Verify and Validate Design
  • Results of Threat Modelling
  • Gaps
  • Alternative Solutions/Mitigations/Compensating Controls
  • Internal or External Third-Party
  • Code Review Methodology

Domain 3: Infrastructure and System Security Architecture

Module 1: Identify Infrastructure and System Security Requirements
  • Deployment Models
  • Information Technology and Operational Technology
  • Physical Security
  • Infrastructure and System Monitoring
  • Infrastructure and System Cryptography
  • Application Security
Module 2: Architect Infrastructure and System Security
  • Physical Security Control Set
  • Platform Security
  • Network Security
  • Storage Security 
  • Data Repository Security
  • Cloud Security
  • Operational Technology 
  • Endpoint Security
  • Secure Shared Services 
  • Third-Party Integrations
  • Infrastructure Monitoring 
  • Content Monitoring
  • Out-of-Band Communications
  • Evaluation of Security Controls for System Components
Module 3: Architect Infrastructure and System Cryptographic Solutions
  • Determine Cryptographic Design Considerations and Constraints
  • Determine Cryptographic Implementation in Various States
  • Plan Key Management Lifecycle

Domain 4: Identity and Access Management (IAM) Architecture

Module 1: Architect Identity Lifecycle
  • Establish and Verify Identity
  • Assign Identifiers to Users and Systems
  • Identity Provisioning and De-Provisioning
  • Identity Management Technologies
Module 2: Architect Identity Authentication
  • Define Authentication Approach
  • Authentication Protocols and Technologies
  • Authentication Control Mechanisms
  • Define Trust Relationships
Module 3: Architect Identity Authorisation
  • Authorisation Concepts and Principles
  • Authorisation Models
  • Authorisation Processes and Workflows
  • Roles, Rights, and Responsibilities Related to System, Application, and Data Access Control
  • Management of Privileged Accounts and Access Rights
  • Authorisation Approaches
Module 4: Architect Identity Accounting
  • Determine Accounting, Analysis, and Forensic Requirements
  • Define Audit Events 
  • Establish Audit Log Alerts and Notifications
  • Log Management 
  • Log Analysis and Reporting
  • Compliance with Policies and Regulations

Show moredown

Who Should Attend this CISSP-ISSAP Training?

This CISSP-ISSAP Training is suitable for experienced security professionals who want to deepen their knowledge of information security architecture and secure system design. The following professionals can benefit from this training:

  • Chief Security Architects
  • Security System Engineers
  • Chief Security Analysts
  • Security Consultants
  • IT Managers & Directors
  • Security Planners
  • Network Architects

Prerequisites for the CISSP-ISSAP Training

There are no formal prerequisites to attend this CISSP-ISSAP Training. However, prior experience in information security architecture or related security domains will help delegates engage effectively with the advanced course content.

CISSP-ISSAP Training Course Overview

CISSP-ISSAP Training helps experienced security professionals develop advanced understanding of information security architecture and secure system design. It covers governance and risk, architecture modelling, cryptography, IAM architecture, and secure integration.

Delegates develop skills in evaluating architectural requirements, selecting controls, assessing design options, and aligning security architecture with business objectives. They also strengthen their understanding of identity, infrastructure, and cryptographic design.

This 4-Day course helps delegates build advanced knowledge of information security architecture within complex environments. They will be better equipped to evaluate secure designs and contribute to architecture-focused security Outcomes. 

CISSP-ISSAP Training Course Objectives

  • To understand information security architecture principles
  • To evaluate security assessment and risk management approaches
  • To align architectural security requirements with business objectives
  • To develop knowledge of secure information-system design
  • To understand governance and compliance within security architecture
  • To evaluate infrastructure, identity, and cryptographic architecture requirements

Learning Outcomes of this CISSP-ISSAP Training

Upon completing this CISSP-ISSAP Training, delegates will understand how to evaluate and design security architecture across governance, infrastructure, IAM, and cryptographic environments. They will be better equipped to support secure architectural decisions and protect critical information assets.

Show moredown

What’s Included in this CISSP-ISSAP Training?

  • World-Class Training Sessions from Experienced Instructors
  • Interactive Learning with 24*7 Support
  • Digital Delegate Pack

Show moredown

Online Instructor-led (3 days)

Online Self-paced (24 hours)

Chief Information Security Officer Training Course Outline

Domain 1: Governance and Risk Management

Module 1: Governance
  • Introduction to Governance
  • Information Security Governance
Module 2: Information Security Management Structure
  • Introduction
  • Sizing
  • Management Structure
Module 3: Principles of Information Security
  • Principles of Information Security
  • CIA Triad
  • Security Vulnerabilities, Threats, Risks, and Exposures
  • Cyberattack Elements
  • Defence-in-depth
Module 4: Risk Management
  • Risk Management Programme
  • Best Practice Frameworks for Risk Management
Module 5: Management and Technical Information Security Elements
  • Management and Technical Information Security Elements
  • Security Programme Plan
  • Security Policies, Standards, and Guidelines
  • Asset Security
  • Identity and Access Management
  • Security Engineering
  • Security Operations
  • Software Development Security
  • Security Assessments and Testing
  • Security Training and Awareness
  • Business Continuity and Disaster Recovery
Module 6: Compliance
  • Compliance
  • Compliance Team
  • Compliance Management
Module 7: Privacy
  • Privacy
  • Privacy Impact Assessment
  • Privacy and Security
Module 8: Laws and Regulatory Drivers
  • Laws and Regulatory Drivers
  • Federal Information Security Modernisation Act
  • Who Does FISMA Apply to?
  • How Does Compliance Impact an Organisation?
  • Defence Federal Acquisition Regulation Supplement 252.204-7012
  • Who Does DFARS 252.204-7012 Apply to?
  • How Does Compliance Impact an Organisation?
  • Clinger-Cohen Act
  • Who Does the Clinger-Cohen Act Apply to?
  • How Does Compliance Impact an Organisation?
  • Who Does PCI DSS Apply to?
  • How Does Compliance Impact an Organisation?
  • Privacy Act of 1974
  • Who Does the Privacy Act Apply to?
  • GRAMM-LEACH-BLILEY ACT
  • Who Does the Gramm-Leach-Bliley Act Apply to?
  • SARBANES-OXLEY ACT
  • Who Does SOX Apply to?
Module 9: Standards and Frameworks
  • ISO/IEC 27000 Series
  • ISO/IEC 27001
  • NIST Cybersecurity Framework
  • Federal Information Processing Standards
  • Privacy Shield
  • COBIT
Module 10: Information Security Trends and Best Practices
  • Information Security Trends and Best Practices
  • Open Web Application Security Project
  • Cloud Security Alliance
  • Centre for Internet Security
Module 11: Ethics
  • Introduction to Ethics

Domain 2: Information Security Controls, Compliance, and Audit Management

Module 12: Information Security Controls
  • Control Fundamentals
  • Control Frameworks
Module 13: Information Security Control Life Cycle Framework
  • NIST Risk Management Framework
  • NIST Cybersecurity Framework
  • ISO/IEC 27000
Module 14: Information Security Control Life Cycle
  • Information Security Control Life Cycle
  • Risk Assessment
  • Design
  • Implementation
  • Assessment
  • Monitoring
Module 15: Exploring Information Security Control Frameworks
  • Exploring Information Security Control Frameworks
  • NIST SP 800-53
  • NIST Cybersecurity Framework
  • ISO/IEC 27002
  • CIS Critical Security Controls
Module 16: Auditing for the CISO
  • Audit Management
  • Audit Process
  • Control Self-assessments
  • Continuous Auditing
  • Specific Types of Audits and Assessments

Domain 3: Security Programme Management and Operations

Module 17: Security Programme Management
  • Security Areas of Focus
  • Security Streams of Work
  • Security Projects
Module 18: Security Programme Budgets, Finance, and Cost Control
  • Establishing the Budget
  • Managing and Monitoring Spending
  • Security Programme Resource Management: Building the Security Team
Module 19: Project Management
  • Project Management Fundamentals
  • Phases of Project Management
    • Initiating
    • Planning
    • Executing
    • Monitoring and Controlling
    • Closing

Domain 4: Information Security Core Competencies

Module 20: Malicious Software and Attacks
  • Malware
  • Scripting and Vulnerability-Specific Attacks
Module 21: Social Engineering
  • Types of Social Engineering Attacks
  • Why Employees are Susceptible to Social Engineering?
  • Social Engineering Defences
Module 22: Asset Security
  • Asset Inventory and Configuration
  • Secure Configuration Baselines
  • Vulnerability Management
  • Asset Security Techniques
Module 23: Data Security
  • Data at Rest
  • Data in Transit
  • Data in Use
  • Data Life Cycle
Module 24: Identity and Access Management
  • Identity and Access Management Fundamentals
  • Identity Management Technologies
  • Authentication Factors and Mechanisms
  • Access Control Principles
  • Access Control Models
  • Access Control Administration
  • Identity and Access Management Life Cycle
Module 25: Communication and Network Security
  • WANs and LANs
  • IP Addressing
  • Network Address Translation
  • Network Protocols and Communications
  • Wireless
  • Network Technologies and Defences
Module 26: Cryptography
  • Cryptography
  • Cryptographic Services
  • Symmetric, Asymmetric, And Hybrid Cryptosystems
  • Hash Algorithms
  • Message Authentication Codes
  • Digital Signatures
Module 27: Cloud Security
  • Cloud Security
  • Cloud Deployment Models
  • Cloud Service Models
  • Cloud Security Risks and Assurance Levels
  • Cloud Security Resources
Module 28: Physical Security
  • Making Security Decisions
  • Physical Security Threats
  • Physical Security Program Planning
  • Physical Security Resources
  • Physical Security Controls
  • Physical Security Auditing and Measurement
Module 29: Personnel Security
  • Personnel Security
  • Software Development Security
  • Integrating Security into the SDLC
  • Security SDLC Roles and Responsibilities
  • Software Vulnerabilities
  • Software Vulnerability Analysis and Assessments
Module 30: Forensics, Incident Handling, and Investigations
  • Relevant Law
  • Logging and Monitoring
  • Incident Response and Investigations
  • Forensics and Digital Evidence
Module 31: Security Assessment and Testing
  • Introduction to Security Assessment and Testing
  • Vulnerability Assessments
  • Penetration Testing
  • Regulatory Compliance Assessments
  • Security Programme Assessments
Module 32: Business Continuity and Disaster Recovery
  • Introduction to Business Continuity and Disaster Recovery
  • Continuity Planning Initiation
  • Business Impact Analysis
  • Identify Preventive Controls
  • Develop Recovery Strategies and Solutions
  • Develop the Plan
  • Test the Plan
  • Maintain the Plan

Domain 5: Strategic Planning, Finance, Procurement, and Vendor Management

Module 33: Strategic Planning
  • Introduction to Strategic Planning
  • Organisational Strategic Planning
  • Organisational Strategic Planning Teams
  • Strategic Planning Process
Module 34: Making Security Decisions
  • Introduction to Making Security Decisions
  • Enterprise Architecture
Module 35: Financial Management
  • Financial Management
  • Accounting and Finance Basics
  • Information Security Annual Budget
Module 36: Procurement and Vendor Management
  • Overview of Procurement and Vendor Management
  • Procurement Core Principles and Processes
  • Types of Contracts
  • Scope Agreements
  • Third-party Vendor Risk Management

Show moredown

Who Should Attend this Chief Information Security Officer Training?

This Chief Information Security Officer Training is suitable for experienced IT and security professionals who want to strengthen knowledge of governance, risk, compliance, security operations, and strategic security management. The following professionals can benefit from this course:

  • Security Consultants
  • IT Security Engineers
  • Chief Information Security Officers (CISOs)
  • Network Architects
  • IT Consultants
  • Risk Managers
  • Compliance Officers

Prerequisites for the Chief Information Security Officer Training

There are no formal prerequisites to attend this Chief Information Security Officer Training. However, prior experience or knowledge in IT, cyber security, governance, or risk management will help delegates engage effectively with the course content.

Chief Information Security Officer Training Course Overview

Chief Information Security Officer Training helps delegates understand the strategic, operational, and governance responsibilities involved in managing organisational information security. It covers governance, risk, compliance, security controls, operations, finance, procurement, and strategic planning.

Delegates develop skills in evaluating security risks, interpreting compliance requirements, overseeing security controls, and supporting security programmes. They also strengthen strategic decision-making across finance, vendor management, and organisational security.

This 3-Day course helps delegates build a structured understanding of senior information security responsibilities. They will be better equipped to contribute to governance, risk, operational oversight, and strategic security decisions.

Chief Information Security Officer Training Course Objectives

  • To understand information security governance and management principles
  • To evaluate risk management and compliance requirements
  • To understand security controls, architecture, and operational security
  • To explore cryptography, IAM, network security, and cloud security
  • To understand security assessment, incident response, and business continuity
  • To develop knowledge of strategic planning, budgeting, procurement, and vendor management

Learning Outcomes of this Chief Information Security Officer Training

Upon completing this CISO Training, delegates will understand how governance, risk, compliance, security operations, and strategic planning contribute to information security management. They will be better equipped to support senior security decisions and oversee organisational security priorities.

Show moredown

What’s Included in this Chief Information Security Officer Training?

  • World-Class Training Sessions from Experienced Instructors
  • Interactive Learning with 24*7 Support
  • Digital Delegate Pack

Show moredown

Online Instructor-led (3 days)

Online Self-paced (24 hours)

Information Systems Security Management Training Course Outline

Module 1: Information Systems

  • Introduction to Information Systems
  • Components
  • Types
  • Acquiring Information Systems and Services
  • Managing Information Systems
  • Information Systems Security and Control
  • Impacts of Information Security Systems

Module 2: Information Security

  • What is Information Security?
  • Need
  • Information Security Triad
  • Threats
  • Active and Passive Attacks
  • Password Security
  • Virtual Private Networks
  • Personal Information Security

Module 3: Information Security Types

  • Application Security
  • Infrastructure Security
  • Cloud Security
  • Cryptography
  • Incident Response
  • Vulnerability Management
  • Disaster Recovery

Module 4: Major Challenges to Information Systems Security

  • Networked Systems
  • Asymmetry Between Defence and Offense
  • Ease-Of-Use Compromises
  • Perimeter Defence
  • Use of COTS Components
  • Threats Posed by Insiders
  • Passive Defence

Module 5: Common Information Security Risks

  • Social Engineering Attacks
  • Advanced Persistent Threats (APT)
  • Insider Threats
  • Cryptojacking
  • Distributed Denial of Service (DDoS)
  • Ransomware
  • Man-in-the-Middle (MitM) Attacks

Module 6: Information Security Technologies

  • Firewalls
  • Security Incident and Event Management (SIEM)
  • Data Loss Prevention (DLP)
  • Intrusion Detection System (IPS)
  • User Behavioural Analytics (UBA)
  • Blockchain Cybersecurity
  • Endpoint Detection and Response (EDR)
  • Cloud Security Posture Management (CSPM)

Show moredown

Who Should Attend this ISSMP Training?

This Information Systems Security Management Professional Training is suitable for delegates who want to strengthen their knowledge of information security, risk, incident response, and system protection. The following individuals can benefit from this training:

  • Information Security Managers
  • Information Security Analysts
  • IT Professionals
  • Compliance Officers
  • Auditors
  • Cybersecurity Engineers
  • DevOps Engineers

Prerequisites for the ISSMP Training

There are no formal prerequisites to attend this ISSMP Training. However, prior knowledge of IT or information security concepts will help delegates engage effectively with the course content.

ISSMP Training Course Overview

Information Systems Security Management Training helps delegates understand how information systems can be protected against security risks and operational challenges. It covers core security principles, system protection, cyber threats, security technologies, and recovery approaches.

Delegates develop skills in recognising security risks, understanding protective technologies, evaluating access controls, and supporting incident response. They also strengthen their knowledge of data protection, network security, and system resilience.

This 3-Day course helps delegates build practical understanding of information systems security management. They will be better equipped to support secure systems, manage security risks, and contribute to organisational security activities.

ISSMP Training Course Objectives

  • To understand core information security principles and system protection
  • To recognise threats, attacks, vulnerabilities, and common security risks
  • To understand authentication, access control, and secure remote connectivity
  • To explore encryption and technologies used to protect information
  • To understand incident response, vulnerability management, and disaster recovery
  • To develop awareness of security practices that support organisational protection

Learning Outcomes of this ISSMP Training

Upon completing this ISSMP Training, delegates will be able to recognise security risks, evaluate protective measures, and support responses to common information security threats. They will also be better equipped to contribute to secure operations, strengthen system protection, and support organisational information security practices.

Show moredown

What’s Included in this Information Systems Security Management Training Course?

  • World-Class Training Sessions from Experienced Instructors
  • Interactive Learning with 24*7 Support
  • Digital Delegate Pack

Show moredown

Not sure which course to choose?

Speak to a training expert for advice if you are unsure of what course is right for you. Give us a call on +44 1344 203 999 or Enquire.

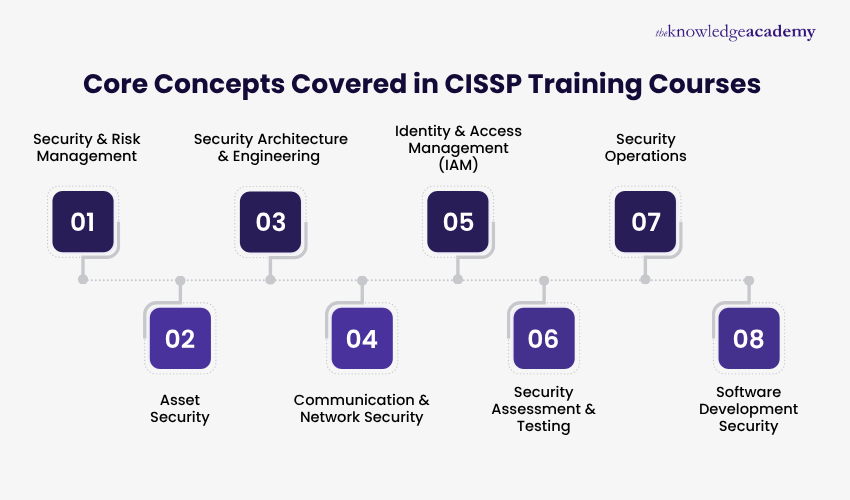
Core Concepts Covered in CISSP Training Courses

Our CISSP Courses cover a broad range of information security areas spanning governance, technical controls, operations, architecture, and secure development. Key concepts include:

Core Concepts Covered in CISSP Training Courses

  • Security and Risk Management: Understand governance, risk, ethics, compliance, and security policies.
  • Asset Security: Explore data classification, ownership, handling, retention, and protection.
  • Security Architecture and Engineering: Examine secure design, cryptography, infrastructure, and system security.
  • Communication and Network Security: Understand secure networks, protocols, segmentation, and connectivity.
  • Identity and Access Management (IAM): Explore authentication, authorisation, identity lifecycles, and access controls.
  • Security Assessment & Testing: Understand audits, vulnerability assessments, testing, and control evaluation.
  • Security Operations: Explore incident management, monitoring, recovery, and operational security controls.
  • Software Development Security: Understand secure development, application security, testing, and software risk.
     

Benefits of Learning CISSP Courses

CISSP Courses help professionals strengthen knowledge across information security, architecture, governance, risk, and security management. The training supports continued development across technical and leadership-focused security responsibilities. Key benefits include:

  • Broader Security Knowledge: Build understanding across technical, governance, risk, and operational security areas.
  • Stronger Risk Awareness: Develop knowledge for identifying risks and evaluating appropriate security controls.
  • Improved Decision-Making: Strengthen the ability to interpret security requirements and support informed decisions.
  • Architecture and Management Insight: Explore approaches relevant to secure system design and security oversight.
  • Professional Development: Build knowledge that can support continued progression across information security responsibilities.
Show more blue-arrow

Package deals for CISSP Courses

Our training experts have compiled a range of course packages on a variety of categories in CISSP Courses, to boost your career. The packages consist of the best possible qualifications with CISSP Courses, and allows you to purchase multiple courses at a discounted rate.

Swipe for more. Don’t miss out!

CISSP Courses FAQs

CISSP, or Certified Information Systems Security Professional, is a globally recognised information security certification covering eight core security domains. The CISSP Certification provides a structured framework for understanding security management, architecture, operations, risk, and related security practices.

Yes, CISSP Training is in demand among professionals developing advanced knowledge in information security, governance, architecture, and risk management. This demand reflects the growing need for professionals who can support complex security responsibilities across organisations.

These CISSP Courses cover a broad range of information security responsibilities, from technical security and risk management to architecture, governance, operations, and strategic security management. They help delegates develop knowledge that can be applied across different security functions and organisational environments.

Yes, The Knowledge Academy provides 24/7 support for these CISSP Courses through phone and email. This support is available before, during, and after training to assist delegates with course-related queries.

After completing this course, delegates will gain skills in risk assessment, access management, security testing, incident response, and secure system design. They will also strengthen their ability to interpret security requirements and support practical security decisions.

Before starting CISSP Courses, prior knowledge of information security, networking, governance, risk management, or security operations is recommended. This background helps delegates understand advanced concepts more effectively and engage confidently with the course content.

To earn the official CISSP Certification, delegates need five years of cumulative work experience in at least two of the eight CISSP domains. Up to one year of this requirement can be satisfied through an eligible degree or approved credential, while professionals without the required experience can become an Associate of ISC2 after passing the CISSP exam and gain the necessary experience within six years.

These CISSP Courses are suitable for experienced IT and cyber security professionals working across security, risk, governance, compliance, architecture, and management. They are particularly relevant to roles such as Security Analysts, Security Managers, Consultants, Architects, and Risk Specialists.

Yes, CISSP Training is aligned with the internationally recognised CISSP Certification and its established security domains. This gives delegates knowledge that is relevant across global information security environments.

The benefits of attending these CISSP Courses include broader security knowledge, stronger analytical capability, and a more structured understanding of technical and managerial security responsibilities. This helps delegates develop a clearer understanding of security requirements, decision-making considerations, and organisational information security responsibilities.

Yes, CISSP knowledge can be applied to cloud security through areas such as access control, architecture, data protection, risk management, and secure operations. These principles help professionals evaluate cloud environments within wider organisational security requirements.

Organisations can benefit from CISSP-trained employees through stronger security awareness, risk evaluation, governance, and technical decision-making. This knowledge can support more consistent security practices across systems, processes, and business operations.

There are no formal prerequisites to attend these CISSP Courses. However, prior knowledge of IT, information security, networking, governance, risk management, or related security concepts will help delegates understand the course content more effectively.

These courses helps career growth by strengthening knowledge relevant to senior technical, architectural, risk, and security management responsibilities. This can support progression into broader information security roles when combined with relevant experience and qualifications.

Industries that hire professionals for advanced information security roles include technology, finance, healthcare, government, consulting, telecommunications, retail, and critical infrastructure. These sectors require skilled professionals to protect systems, data, networks, and digital services.

These CISSP Courses are available through classroom, online instructor-led, and self-paced learning formats. These options allow delegates to choose a training format that suits their schedule and learning preferences.

Yes, Certified Information Systems Security Professional (CISSP) is relevant for professionals working in security management because it covers governance, risk, policy, operations, architecture, and access control. This broad coverage helps professionals understand how technical, operational, and managerial security responsibilities work together across an organisation.

Security operations are addressed through topics such as monitoring, incident management, threat intelligence, vulnerability management, recovery, and business continuity. These areas help delegates understand how day-to-day security activities support ongoing protection and response.

Security assessment and testing are significant because they help delegates identify vulnerabilities, evaluate security controls, and determine whether protective measures are working effectively. This training develops that understanding through vulnerability assessments, penetration testing, audits, control testing, and analysis of security test results.

Identity and Access Management plays a key role in helping delegates understand how access to systems, applications, services, and information should be controlled. The training covers authentication, authorisation, provisioning, access models, privilege management, and identity lifecycles.

The Knowledge Academy in Algeria offers structured CISSP Courses with experienced instructors, flexible learning options, and broad security coverage. Delegates also receive dedicated support and learning resources to strengthen their development across different information security responsibilities.

Please see our CISSP Courses available in Algeria

The Knowledge Academy is one of the Leading global training provider for CISSP Courses.

The training fees for CISSP Courses in Algeria starts from $4695

Show more down

Why we're the go to training provider for you
icon

Best price in the industry

You won't find better value in the marketplace. If you do find a lower price, we will beat it.
icon

Trusted & Approved

Recognised by leading certification bodies, we deliver training you can trust.
icon

Many delivery methods

Flexible delivery methods are available depending on your learning style.
icon

High quality resources

Resources are included for a comprehensive learning experience.
barclays Logo
deloitte Logo
Thames Water Logo

"Really good course and well organised. Trainer was great with a sense of humour - his experience allowed a free flowing course, structured to help you gain as much information & relevant experience whilst helping prepare you for the exam"

Joshua Davies, Thames Water

santander logo
bmw Logo
Google Logo
cross

BIGGEST HALLOWEEN SALE!

halloween-sale GET UPTO 40% OFF!

* WHO WILL BE FUNDING THE COURSE?

close

close

Thank you for your enquiry!

One of our training experts will be in touch shortly to go over your training requirements.

close

close

Press esc to close

close close

Back to course information

Thank you for your enquiry!

One of our training experts will be in touch shortly to go overy your training requirements.

close close

Thank you for your enquiry!

One of our training experts will be in touch shortly to go over your training requirements.