Who Should Attend this ISO 27001 Internal Auditor Training Course?
The ISO 27001 Internal Auditor Course is designed for professionals involved in internal auditing, information security management, and compliance roles. This course can be beneficial for a wide range of professionals, including:
- Internal Auditors
- Information Security Managers
- IT Managers
- Cybersecurity Engineers
- Risk Managers
- Compliance Officers
- ISMS Managers
- Governance Professionals
Prerequisites of the ISO 27001 Internal Auditor Training Course
There are no formal prerequisites for this ISO 27001 Internal Auditor Course. However, familiarity with Information Security principles and concepts can be beneficial for the delegates.
ISO 27001 Internal Auditor Training Course Overview
ISO 27001 Internal Auditor Course develops the skills required to conduct internal audits of an Information Security Management System against ISO/IEC 27001 requirements. It covers audit principles, evidence evaluation, nonconformities, reporting, and continual improvement.
Delegates will develop practical knowledge of audit planning, evidence review, audit techniques, findings, and reporting. They will also understand how internal audits support ISMS performance, corrective action, and continual improvement.
This 2-Day course by The Knowledge Academy helps delegates apply ISO 27001 internal auditing practices in organisational environments. Delegates will be better prepared to conduct structured audits, communicate findings, and support effective ISMS improvement.
ISO 27001 Internal Auditor Training Course Objectives
- To understand ISO/IEC 27001 requirements and the structure of an ISMS
- To understand internal audit principles, standards, techniques, and responsibilities
- To plan and prepare ISO 27001 internal audits effectively
- To review audit evidence, documents, records, and organisational processes
- To classify audit findings and prepare clear internal audit reports
- To support nonconformity resolution, corrective action, and continual improvement
After completing this course, delegates will be able to plan, conduct, and report internal audits of an ISMS against ISO/IEC 27001 requirements. They will also be better prepared to identify nonconformities, evaluate audit evidence, and support corrective action and continual improvement.
Benefits of ISO 27001 Internal Auditor Training Course
ISO 27001 Internal Auditor Training helps professionals build practical skills for reviewing an Information Security Management System against ISO/IEC 27001 requirements. It strengthens their ability to plan audits, assess evidence, identify nonconformities, communicate findings, and support continual improvement. Key benefits include:
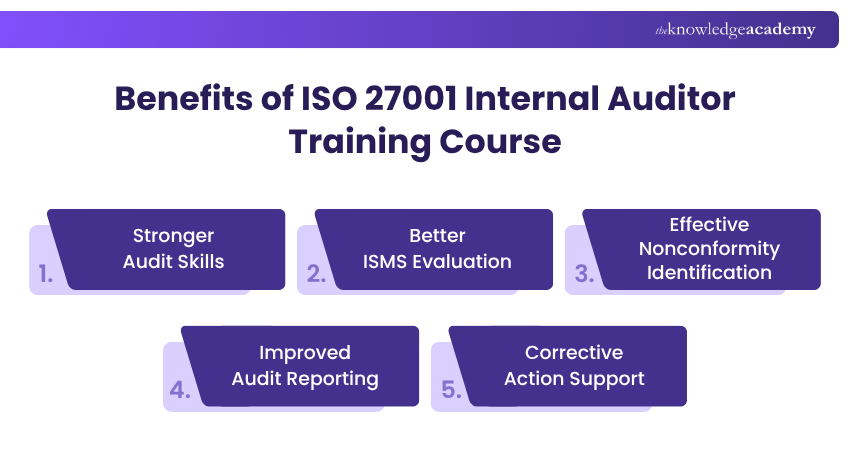
- Stronger Audit Skills: Develop practical knowledge of audit principles, techniques, planning, execution, and reporting.
- Better ISMS Evaluation: Understand how to review ISMS processes, documented information, risk activities, and organisational practices.
- Effective Nonconformity Identification: Learn to identify, classify, and document audit findings accurately.
- Improved Audit Reporting: Build skills for preparing clear audit reports, conclusions, and supporting documentation.
- Corrective Action Support: Understand how audit findings contribute to corrective action and continual improvement.
Career Opportunities After Completing ISO 27001 Internal Auditor Training Course
Completing this training can support professionals seeking roles involving information security auditing, compliance, risk, and ISMS assurance. Potential career opportunities include:
- ISO 27001 Internal Auditor: Conduct internal ISMS audits, review evidence, identify findings, and prepare audit reports.
- Information Security Auditor: Evaluate information security processes and assess their alignment with organisational and ISO/IEC 27001 requirements.
- Compliance Analyst: Support compliance activities by reviewing processes, documentation, risks, and corrective actions.
- Risk and Assurance Analyst: Assist with risk assessment, assurance activities, audit evidence, and organisational controls.
- ISMS Manager: Support the operation, evaluation, and continual improvement of an Information Security Management System.




 If you miss out, enquire to get yourself on the waiting list for the next day!




 If you wish to make any changes to your course, please


