Who Should Attend this ISO 27001 Lead Implementer Training?
This ISO 27001 Lead Implementer Course is suitable for professionals involved in establishing, implementing, managing, or improving Information Security Management Systems in line with ISO 27001 requirements. The following professionals can benefit from attending this course:
- Security Consultants
- Compliance Officers
- Information Security Managers
- Risk Managers
- Cybersecurity Engineers
- Auditors
- Compliance Managers
Prerequisites for the ISO 27001 Lead Implementer Training
There are no formal prerequisites to attend this ISO 27001 Lead Implementer Course. However, familiarity with ISO 27001 standard and information security principles will be beneficial for the delegates.
ISO 27001 Lead Implementer Training Overview
ISO 27001 Lead Implementer Training provides delegates with the skills required to manage an Information Security Management System (ISMS) in accordance with ISO 27001. It focuses on risk management, control implementation, and continual improvement practices.
This training enhances delegates’ ability to lead ISMS implementation projects and strengthen organisational information security frameworks. It builds structured competence in managing documentation, audits, and risk treatment processes.
This 3-Day course offered by The Knowledge Academy enables delegates to apply ISO 27001 principles confidently within real-world environments. Delegates will be able to coordinate implementation activities, support employee awareness, monitor ISMS performance, and address nonconformities.
ISO 27001 Lead Implementer Training Course Objectives
- To understand ISO 27001 principles, requirements, and terminology
- To perform risk assessments and define appropriate risk treatment plans
- To establish, implement, and manage an effective ISMS
- To document and maintain compliance with ISO 27001 standards
- To implement Information Security procedures and controls within an organisation
- To apply continual improvement processes within the ISMS framework
Upon completing this course, delegates will be equipped to establish, implement, manage, and improve an ISMS within an organisation. They will also develop the confidence to manage risk treatment, apply controls, support internal audits, and lead ISO 27001 implementation activities within an organisation.
Key Benefits of this ISO 27001 Lead Implementer Certification
This ISO 27001 Lead Implementer Certification helps professionals strengthen their ability to establish, manage, and improve Information Security Management Systems in line with ISO 27001 requirements. Key benefits include:
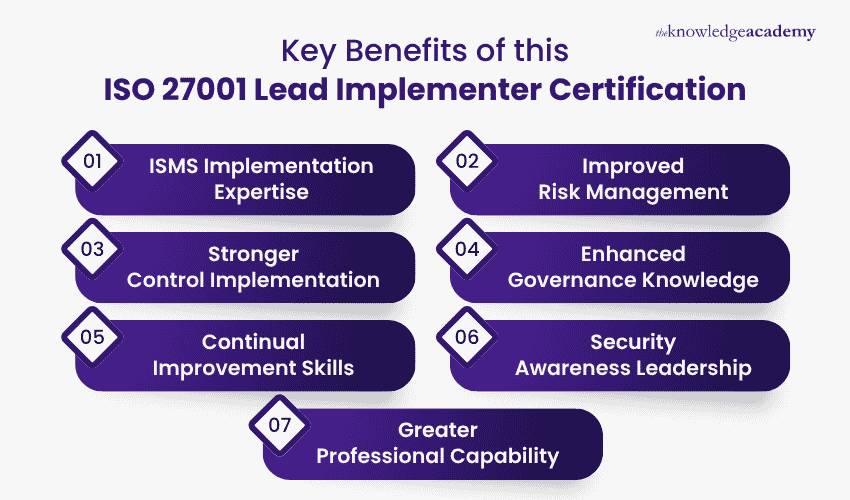
- ISMS Implementation Expertise: Develop the knowledge required to establish, implement, manage, and improve an Information Security Management System.
- Improved Risk Management: Build skills in conducting risk assessments, evaluating risks, and applying appropriate risk treatment approaches.
- Stronger Control Implementation: Learn how to apply frameworks, procedures, and controls that support organisational information security objectives.
- Enhanced Governance Knowledge: Understand leadership responsibilities, organisational roles, policies, and governance requirements within an ISMS.
- Continual Improvement Skills: Develop the ability to support corrective actions, performance evaluation, management reviews, and continual ISMS improvement.
- Security Awareness Leadership: Gain knowledge of training and awareness programmes that help employees understand their information security responsibilities.
- Greater Professional Capability: Strengthen practical expertise in ISO 27001 implementation, risk management, governance, and ISMS management to support broader information security responsibilities.
Career Opportunities After Completing this ISO 27001 Lead Implementer
Completing this ISO 27001 Lead Implementer Course can support career progression across information security, ISMS implementation, risk management, governance, and compliance roles. Potential career opportunities include:
- Information Security Manager: Oversee information security practices, ISMS implementation, risk treatment, and continual improvement activities.
- ISMS Manager: Manage the establishment, operation, monitoring, and improvement of an organisation’s Information Security Management System.
- Information Security Consultant: Support organisations in implementing ISO 27001 requirements, defining ISMS scope, applying controls, and improving security practices.
- Risk Manager: Assess information security risks, evaluate their potential impact, and support appropriate risk treatment approaches.
- Compliance Manager: Support compliance with ISO 27001 requirements by managing policies, documented information, controls, and governance activities.
- Internal Auditor: Review ISMS processes, evaluate conformity, assess documented information, and support corrective actions and continual improvement.




 If you miss out, enquire to get yourself on the waiting list for the next day!




 If you wish to make any changes to your course, please


