


We may not have the course you’re looking for. If you enquire or give us a call on 01344203999 and speak to our training experts, we may still be able to help with your training requirements.
Home
 Resources
IT Security & Data Protection
What is a Cyber Security Framework? How to Protect Your Data
Resources
IT Security & Data Protection
What is a Cyber Security Framework? How to Protect Your Data
What is a Cyber Security Framework? How to Protect Your Data
ByJohn DaviesLast updated on: 22 September 2026
A Cyber Security Framework outlines structured policies and controls to identify, prevent, detect, respond to, and recover from cyber threats effectively. It provides a clear, standardised approach for managing security risks, protecting sensitive information, and ensuring operational continuity across digital environments.
A single cyber incident can compromise data, disrupt operations, and erode trust in seconds. In today’s digital landscape, protecting information requires more than reactive measures, it demands a structured security strategy.
A Cyber Security Framework provides that structure by defining clear functions and controls to manage risks. In this blog, we explain what Cyber Security Framework is, its core components, and how it helps organisations protect their data effectively.
What is Cyber Security Framework?
Most companies today emphasise developing concrete solutions for cyber-attacks across their systems, networks, software and devices. A Framework in Cyber Security provides plans and strategies for determining and building risk resistance by setting Cyber Security controls to increase the effectiveness of security measures.to increase the effectiveness of security measures.
Therefore, adopting different strategies to protect organisations from estimated risks and attacks is essential. However, there is no standardised platform to ensure Cyber Security; many alternatives exist. Understanding the Difference Between Antivirus and Internet Security helps organisations decide which solutions to implement based on their specific security needs.
Why are Cyber Security Frameworks Important for Your Organisation?
Cyber Security Frameworks are mandatory as they offer a systematic method of identifying, managing, and minimising security risks. Organisations do not respond to threats in a random way but adhere to specific processes that enhance security and efficiency in preparedness.
They also heighten compliance, accountability and resiliency of operations by aligning the security practice according to accepted standards. This will provide uniformity in risk control, improved response to incidents, and increased safeguarding of sensitive organisational information.
Identify, assess, and mitigate digital risks effectively with our Cyber Security Risk Management Course- Join now!
Top Cyber Security Frameworks to Consider
Choosing an appropriate Cyber Security Framework is at the core of enhancing security posture in your organisation. With the available multiple standards, knowing their characteristic of concentration and range of scope will allow you to select one of the standards that fits your regulatory, operational, and risk management requirements.
Ten of the most commonly adopted Cyber Security Frameworks that organisations use to improve protection and compliance are listed below:
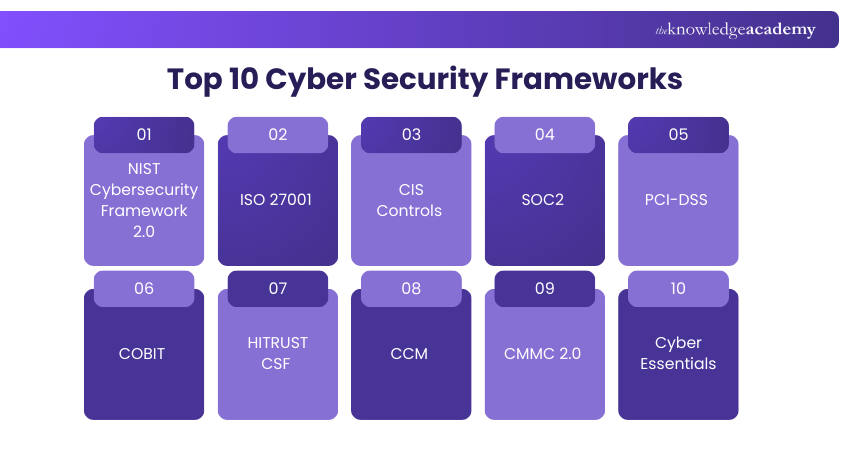
1) NIST Cybersecurity Framework 2.0
The NIST Cybersecurity Framework 2.0 gives a wide-range advice on cyber risk management. It is designed with six major functions, namely Govern, Identify, Protect, Detect, Respond, and Recover. These functions assist organisations in incorporating governance, putting various safeguards, identifying an incident at the early stage and being resilient by being able to respond and recover planning.
2) ISO 27001
ISO 27001 is a globally recognised standard based on designing an Information Security Management System (ISMS). It mandates organisations to spot risks, put security control measures in place and keep a track of the information security practises and improvements. This Cyber Security Framework indicates that there are an organised risk management and a security to for sensitive information safeguarded.
3) CIS Controls
CIS Controls gives a sequence of actions with priorities available in the fight against the common cyber threats. They involve the necessary tasks, including asset listing, highly secured settings, and twenty-four monitoring. The framework provides viable and practical controls that can be used by organisations that want organised yet flexible security enhancements.
4) SOC2
SOC 2 assesses the organisational controls in the areas of security, availability, processing integrity, confidentiality and privacy. The assessment performed by an audit is to identify the fulfilment of the trust service requirements in defined systems and processes. It has a specific application where service givers are dealing with consumer records.
5) PCI-DSS
PCI-DSS outlines the security measures of organisations that process, store, or transmit information in payment cards. It requires encryption, access control, monitoring of the network, and a protective firewall. Compliance ensures secure handling of cardholder data and reduces fraud risk.
6) COBIT
COBIT is an information technology governance and management Cyber Security Framework which matches IT objectives to business objectives. It consists of control objectives, process models and maturity assessments. The framework improves accountability, transparency, and performance of IT governance.
7) HITRUST CSF
The HITRUST Common Security Framework (CSF) is a certifiable framework of standards, which is a combination of ISO, NIST, HIPAA and GDPR. This Cyber Security Framework will provide a dynamic method of compliance and risk management. Its combined structure allows its application in industries that process sensitive health and regulatory data.
8) CCM
The CCM is a cloud-based security controls model created to deal with cloud governance, risk and compliance. CCM Cyber Security Framework offers organised areas that govern safe cloud service deployment. Many companies across the world rely on CCM as a measure of cloud security practises.
9) CMMC 2.0
The Cybersecurity Maturity Model Certification (CMMC) 2.0 is a security model that was initiated by the U.S. Department of Defence to enhance security in the Defence Industrial Base. It establishes several maturity levels with particular practises needed. This Cyber Security Framework helps in ascertaining that contractors comply with the set security standards when using sensitive defence information.
10) Cyber Essentials
The Cyber Essentials is a certification scheme supported by the UK government and aims to secure organisations against general cyber attacks. It presupposes the use of minimum controls on firewalls, secure settings, and software upgrades. The scheme aids organisations in portraying some basic cybersecurity preparedness.
Develop core digital investigation skills with our Computer Forensics Foundation Training Course- Join now!
How to Implement and Maintain a Cyber Security Framework
A Cyber Security Framework is a structured process that needs to be executed in a disciplined manner and monitored continuously. It should be incorporated into the daily operations to deliver measurable risk reduction after it is chosen.
These are the keyways to implement and maintain a Cybersecurity Framework:
1) Identify Scope and Objectives: Provide an alignment between the framework and business objectives, risk appetite, and regulatory provisions.
2) Establish Governance Structures: Establish leadership and operational roles and responsibilities as well as accountability.
3) Risk Assessment: Determine assets, threats, vulnerabilities, and focus on mitigation processes.
4) Establish Controls and Policies: Have deployed administrative, physical, and technical controls that are necessitated by the framework.
5) Train Employees: Awareness and compliance with security policies and best practises of the workforce.
6) Carry Out Frequent Audits: determine performance, identify flaws and assess performance conformance.
7) Monitor And Improve Continuously: Enhance controls, policies and procedures to meet new threats and business requirements.
Strengthen your breach response strategy with our Incident Response Training Course - Sign up now!
John Davies creates security-focused content that helps organisations understand digital risks and establish appropriate safeguards. His practical explanations connect regulatory expectations, governance principles and security controls with wider organisational priorities.
View Detail

 If you wish to make any changes to your course, please


